

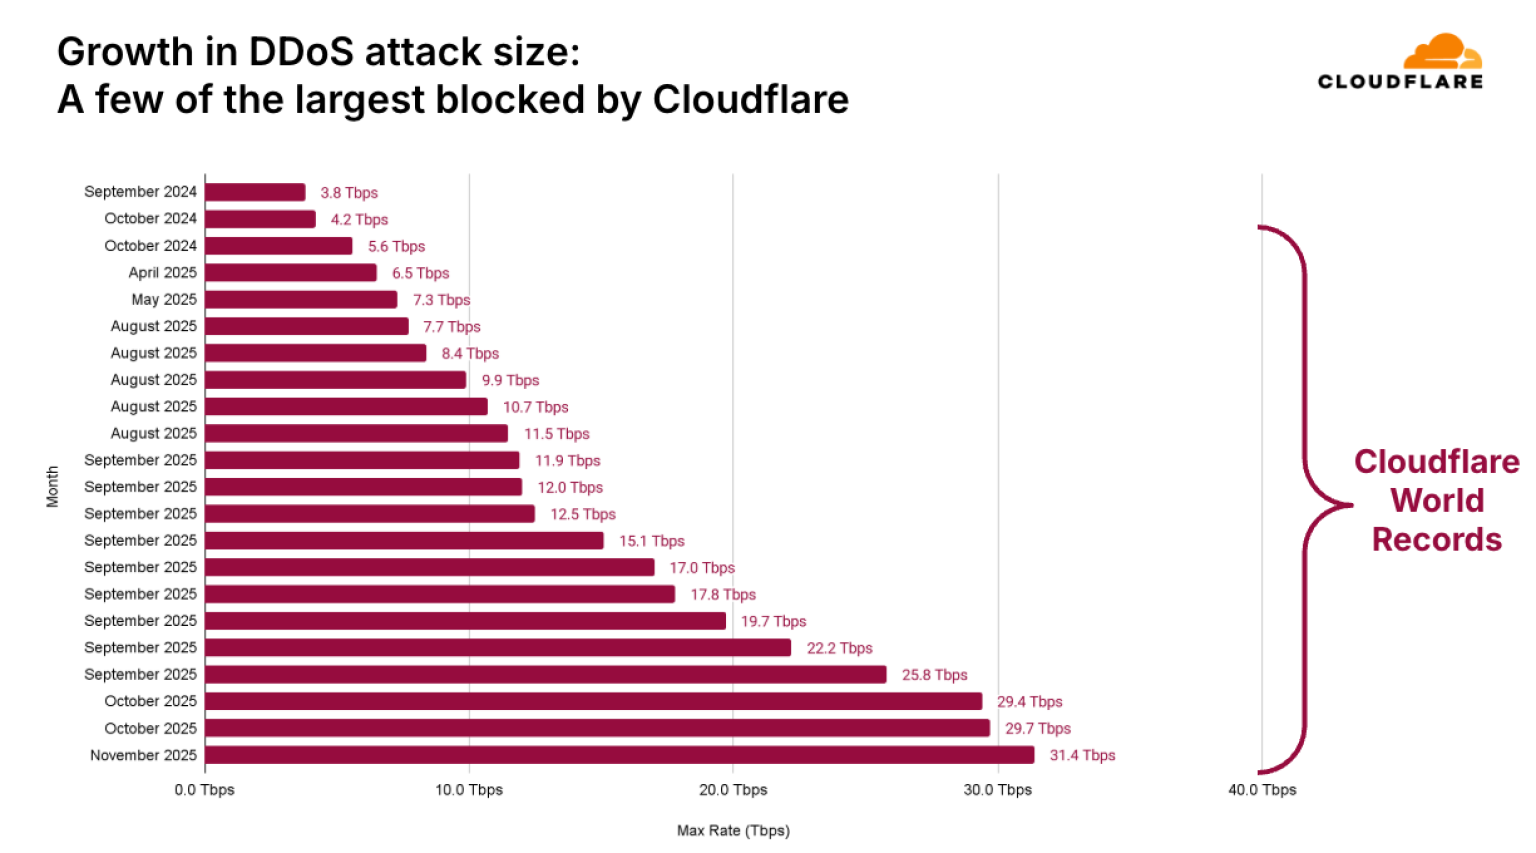
AISURU/Kimwolf botnet hit a record 31.4 Tbps DDoS attack lasting 35 seconds in Nov 2025, which Cloudflare automatically detected and blocked.
The AISURU/Kimwolf botnet was linked to a record-breaking DDoS attack that peaked at 31.4 Tbps and lasted just 35 seconds. Cloudflare said the November 2025 incident was part of a surge in hyper-volumetric HTTP DDoS attacks observed in late 2025, all automatically detected and mitigated.
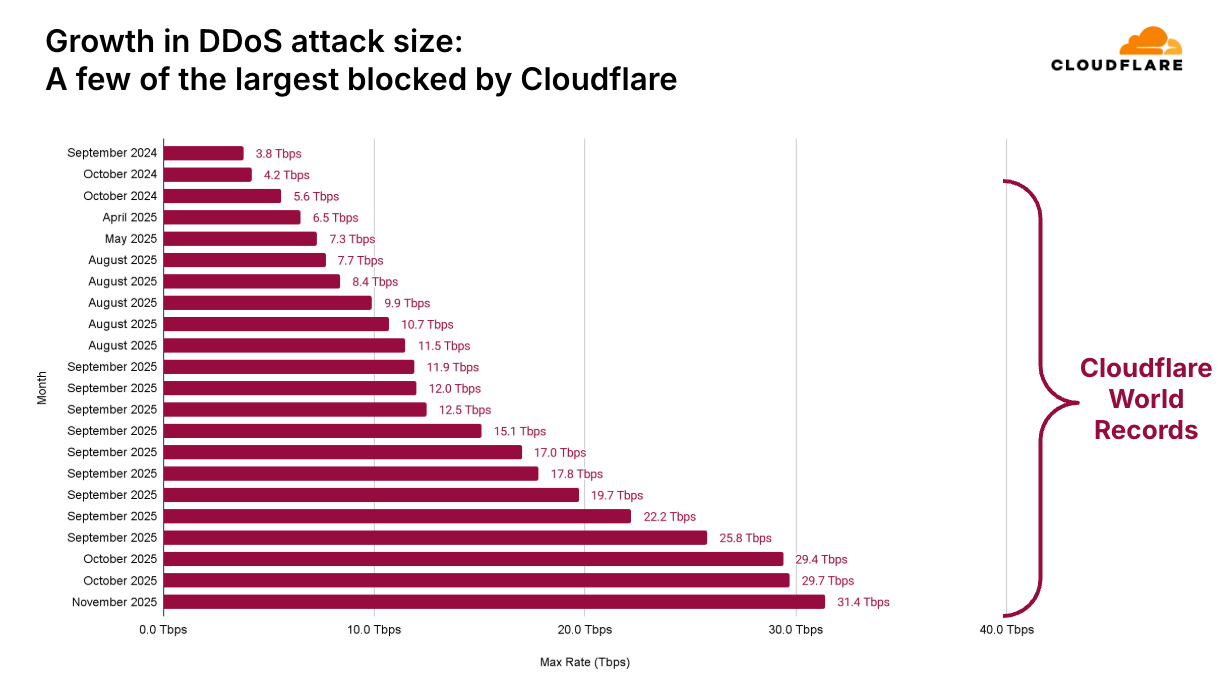
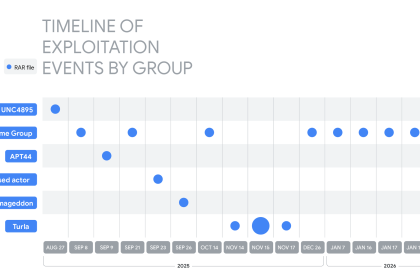
“Throughout 2025, Cloudflare observed a continuous increase in hyper-volumetric DDoS attacks. In 2025 Q4, hyper-volumetric attacks increased by 40% compared to the previous quarter.” reads the report published by Cloudflare. “As the number of attacks increased over the course of 2025, the size of the attacks increased as well, growing by over 700% compared to the large attacks seen in late 2024, with one reaching 31.4 Tbps in a DDoS attack that lasted just 35 seconds. The graph below portrays the rapid growth in DDoS attack sizes as seen and blocked by Cloudflare — each one a world record, i.e. the largest ever disclosed publicly by any company at the time.”


Acting as a DDoS-for-hire service, Aisuru avoids government and military targets, but broadband providers faced serious disruptions from attacks exceeding 1.5Tb/sec from infected customer devices.
Like other TurboMirai botnets, Aisuru incorporates additional dedicated DDoS attack capabilities and multi-use functions, enabling operators to carry out other illicit activities, including credential stuffing, artificial intelligence (AI)-driven web scraping, spamming, and phishing.
Attacks use UDP, TCP, and GRE floods with medium-sized packets and randomized ports/flags. Over 1Tb/sec traffic from compromised CPEs disrupts broadband, and 4gpps+ floods have caused router line card failures.
Kimwolf is a newly discovered Android botnet linked to the Aisuru botnet that has infected over 1.8 million devices and issued more than 1.7 billion DDoS attack commands, according to XLab.
Maingear Instant Trade-In Program Maximizes Gaming PC Value and Hardware Upgrades
Maingear Launches Instant Trade-In Program for Gaming PC Buyers American custom and…
South Korea’s Lee says AI appears to have been used in bank hacks
SEOUL – South Korean President Lee Jae Myung said on Tuesday that…
New Fluke USB Acoustic Imager Smartphone Camera
Fluke has launched a more affordable acoustic imaging camera, model II01, that…
North Korea tests new weapon system (PHOTOS)
DPRK media released photos showing the launch of a road-mobile missile tipped…
U.S. CISA adds a flaw in multiple Fortinet products to its Known Exploited Vulnerabilities catalog
The U.S. Cybersecurity and Infrastructure Security Agency (CISA) adds a flaw in…
U.S. Expands F-35 Fighter Jet Support Network With $871 Million for Dispersed Combat Operations
The United States is expanding the sustainment network supporting its F-35 Lightning…
The Kimwol Android botnet primarily targets TV boxes, compiled using the NDK and equipped with DDoS, proxy forwarding, reverse shell, and file management functions. It encrypts sensitive data with a simple Stack XOR, uses DNS over TLS to hide communication, and authenticates C2 commands with elliptic curve digital signatures. Recent versions even incorporate EtherHiding to resist takedowns via blockchain domains.
Kimwolf follows a naming pattern of “niggabox + v[number]”; versions v4 and v5 have been tracked. By taking over one C2 domain, researchers observed around 2.7 million IPs interacting over three days, indicating a likely infection scale exceeding 1.8 million devices. Its infrastructure spans multiple C2s, global time zones, and versions, making it hard to estimate the total number of infections.
The botnet borrows the code from the Aisuru family, however, operators redesigned it to evade detection. Its primary function is traffic proxying, though it can execute massive DDoS attacks, as seen in a three-day period issuing 1.7 billion commands between November 19 and 22.
In Q4 2025, the largest DDoS attacks mainly targeted Cloudflare customers in the Telecommunications, Service Providers, and Carriers sector, followed by Gaming and Generative AI services. Cloudflare’s own infrastructure was also attacked using HTTP floods, DNS attacks, and UDP floods. Globally, China, the United States, Germany, and Brazil remained among the most targeted countries, while Hong Kong and especially the United Kingdom saw sharp increases in attacks.
Regarding attack origins, Bangladesh became the top source of DDoS traffic, overtaking Indonesia, with notable rises also seen from Ecuador and Argentina.
Most DDoS attacks in Q4 2025 originated from IPs linked to major cloud platforms like DigitalOcean, Microsoft, Tencent, Oracle, and Hetzner, mostly in the U.S. Telcos in Asia-Pacific also contributed. Attacks are global, using thousands of source networks. Cloudflare offers a free DDoS Botnet Threat Feed, with 800+ networks collaborating to identify and shut down abusive IPs.
“DDoS attacks are rapidly growing in sophistication and size, surpassing what was previously imaginable. This evolving threat landscape presents a significant challenge for many organizations to keep pace.” concludes the report. “Organizations currently relying on on-premise mitigation appliances or on-demand scrubbing centers may benefit from re-evaluating their defense strategy.”