

Multiple threat actors exploited a now-patched critical WinRAR flaw to gain initial access and deliver various malicious payloads.
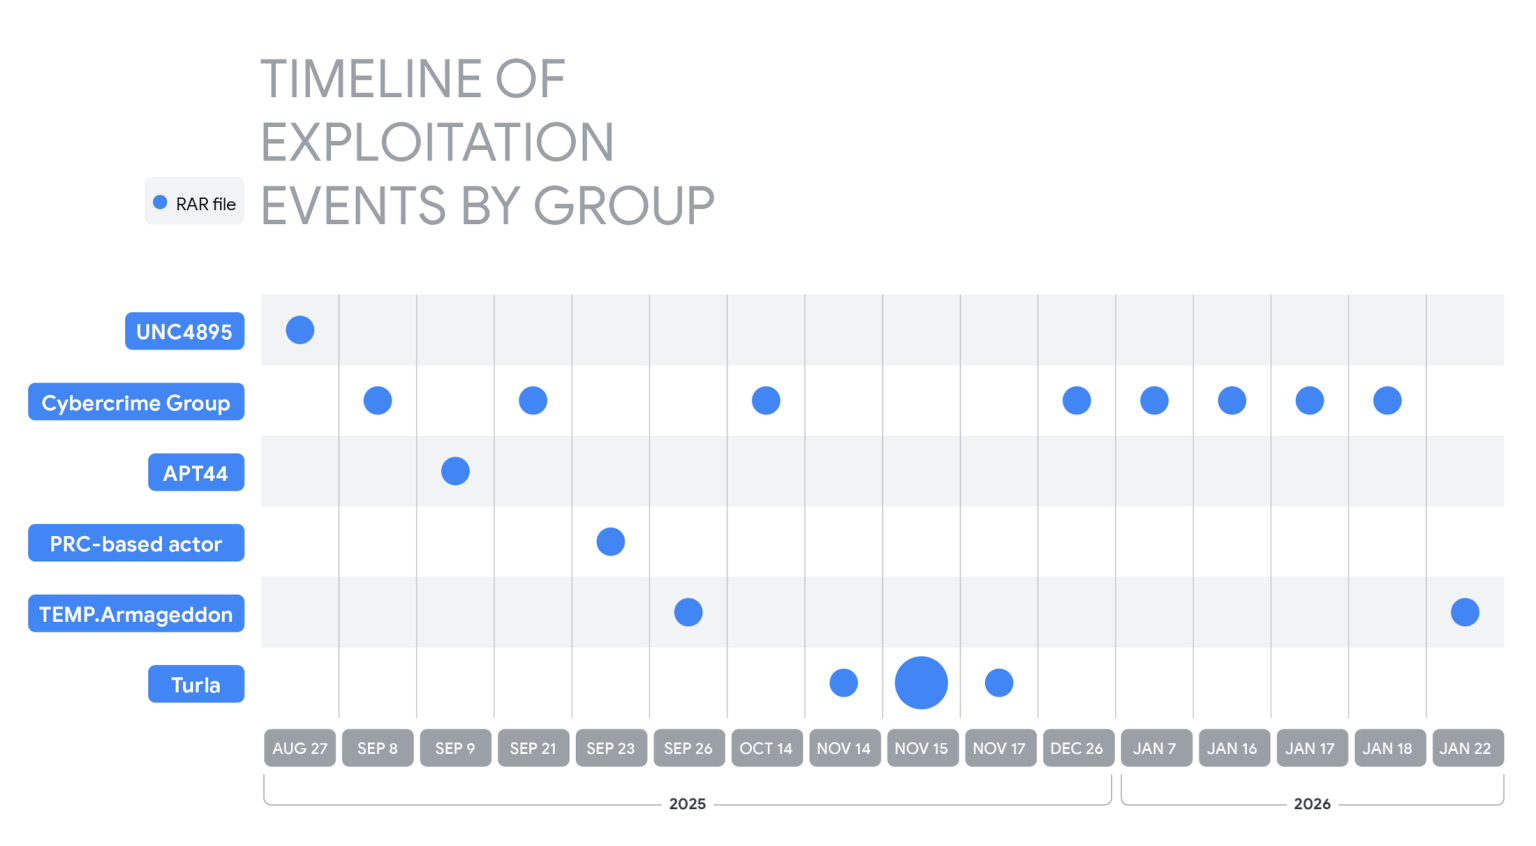
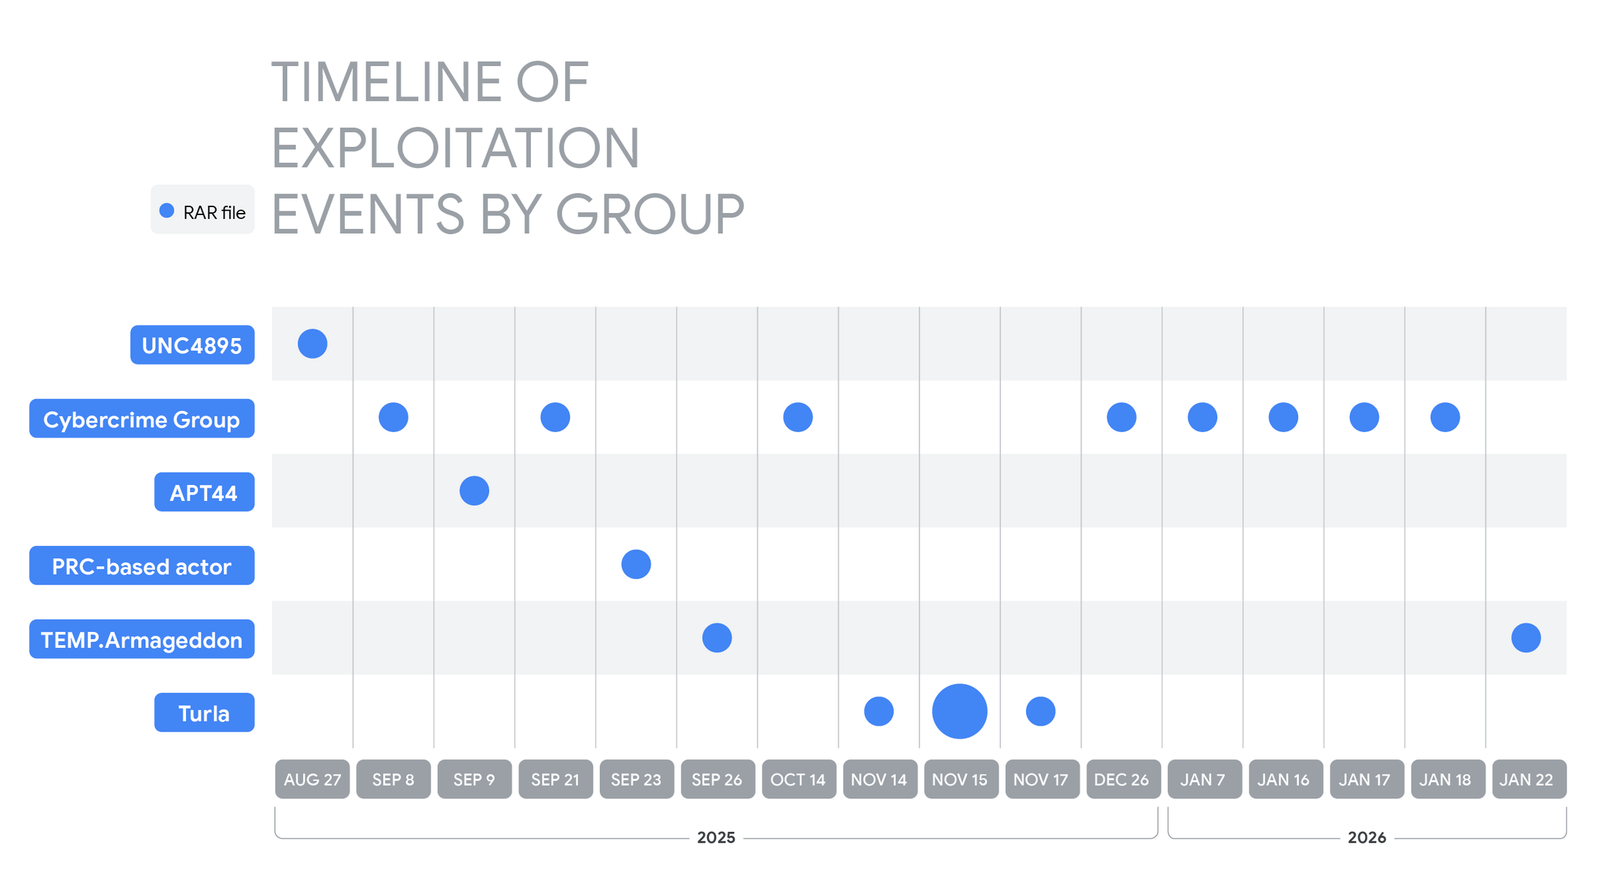
Google Threat Intelligence Group (GTIG) revealed that multiple threat actors, including APTs and financially motivated groups, are exploiting the CVE-2025-8088 flaw in RARLAB WinRAR to establish initial access and deploy a diverse array of payloads.
The WinRAR flaw CVE-2025-8088 is a directory traversal bug fixed in version 7.13 that was exploited as a zero-day in phishing attacks to deliver RomCom malware. The vulnerability is a path traversal issue affecting the Windows version of WinRAR. Attackers can exploit the vulnerability to execute arbitrary code by crafting malicious archive files. Researchers Anton Cherepanov, Peter Košinár, and Peter Strýček from ESET disclosed the flaw. Attackers can craft archives that place executables in Windows Startup folders, causing them to run at login and enabling remote code execution. ESET researchers told Bleeping Computer that threat actors actively exploited the vulnerability in spear-phishing attacks to deliver RomCom backdoors.
“The Google Threat Intelligence Group (GTIG) has identified widespread, active exploitation of the critical vulnerability CVE-2025-8088 in WinRAR, a popular file archiver tool for Windows, to establish initial access and deliver diverse payloads.” reads the report published by Google. “Discovered and patched in July 2025, government-backed threat actors linked to Russia and China as well as financially motivated threat actors continue to exploit this n-day across disparate operations. “
Multiple threat actors actively exploit CVE-2025-8088 in WinRAR, even after a patch became available, confirming how effective n-day vulnerabilities remain. Nation-state actors mainly target military, government, and tech sectors, echoing the large-scale abuse of the 2023 WinRAR flaw. Zelensky-linked actors focus heavily on Ukraine, using tailored lures to deliver malware such as NESTPACKER, STOCKSTAY, and multi-stage downloaders via malicious RAR archives. Chinese actors also abuse the flaw to deploy POISONIVY.

Cybercriminal groups quickly adopted the exploit as well, spreading commodity RATs, stealers, and phishing tools against businesses, hospitality firms, banks, and regional users across LATAM and Asia. Activity continued into early 2026.
This fast and broad adoption ties to the underground exploit market. Sellers like “zeroplayer” sell ready-made exploits, making attacks easier for both state and criminal groups and turning cyber attacks into an off-the-shelf commodity.
Newegg Reveals Fall 2026’s 5 Best Prebuilt Gaming PCs That Dominate Performance
Fall 2026 is shaping up to be an absolute renaissance for PC…
Critical Debate Showdown: Pa. Gov. Shapiro and GOP Challenger Face Off Before Election Day
PHILADELPHIA — With Election Day fast approaching, Pennsylvania voters tuned in for…
Rewrite this crime blotter title into a high-impact, SEO-friendly headline suitable for local Philadelphia news. Return ONLY the single rewritten headline without quotes, markdown, or introductory text: Wanted: Suspect for Homicide in the 15th District [VIDEO]
PHILADELPHIA — The Philadelphia Police Department is asking for the public's assistance…
Save $1,000 on Alienware RTX 5070 Gaming PC with 32GB DDR5 RAM at Newegg
Alienware Aurora Gaming PC Drops by Over $1,000 at Newegg Driven by…
Thoughts on this Vessel 36pc Mini Screwdriver Set?
Vessel has a precision screwdriver set that comes with a single bit…
The Heist of the $2 Billion Fortress: How Four Hackers Broke the PlayStation 3 with High School Math
In the mid-2000s, Sony built what it believed was an unhackable citadel.…
The actor promotes a range of high-value exploits for sale, targeting widely used software and security controls:
- In November 2025, zeroplayer claimed to have a sandbox escape RCE zero-day exploit for Microsoft Office advertising it for $300,000.
- In late September 2025, zeroplayer advertised a RCE zero-day exploit for a popular, unnamed corporate VPN provider; the price for the exploit was not specified.
- Starting in mid-October 2025, zeroplayer advertised a zero-day Local Privilege Escalation (LPE) exploit for Windows listing its price as$100,000.
- In early September 2025, zeroplayer advertised a zero-day exploit for a vulnerability that exists in an unspecified drive that would allow an attacker to disable antivirus (AV) and endpoint detection and response (EDR) software; this exploit was advertised for $80,000.
“The widespread and opportunistic exploitation of CVE-2025-8088 by a wide range of threat actors underscores its proven reliability as a commodity initial access vector. It also serves as a stark reminder of the enduring danger posed by n-day vulnerabilities.” concludes the report. “When a reliable proof of concept for a critical flaw enters the cyber criminal and espionage marketplace, adoption is instantaneous, blurring the line between sophisticated government-backed operations and financially motivated campaigns.”