

Fortinet confirmed attacks are bypassing FortiCloud SSO authentication, affecting even fully patched devices, similar to recent SSO flaws.
Fortinet confirmed attacks bypass FortiCloud SSO on fully patched devices. Threat actors automate firewall changes, add users, enable VPNs, and steal configs, in campaigns resembling December 2025 exploits of critical FortiCloud SSO flaws.
Arctic Wolf researchers reported a new automated attack cluster observed since January 15, 2026, targeting FortiGate devices. Attackers created generic accounts for persistence, enabled VPN access, and exfiltrated firewall configurations. The activity resembles a December 2025 campaign involving admin SSO logins and config theft. Arctic Wolf has detections in place and is monitoring the evolving threat.
“Starting on January 15, 2026, Arctic Wolf began observing a new cluster of automated malicious activity involving unauthorized firewall configuration changes on FortiGate devices.” reads the report published by Arctic Wolf. “This activity involved the creation of generic accounts intended for persistence, configuration changes granting VPN access to those accounts, as well as exfiltration of firewall configurations. “
In December 2025, Fortinet disclosed two critical SSO authentication bypass flaws, tracked as CVE-2025-59718 and CVE-2025-59719, which are improper verification of cryptographic signature issues.
Threat actors started exploiting the two critical flaws in Fortinet products days after patch release, Arctic Wolf warned.
Arctic Wolf researchers observed attackers began exploiting critical Fortinet authentication bypass flaws on December 12, just three days after patches were issued. The attacks involved malicious SSO logins on FortiGate devices, mainly targeting admin accounts from multiple hosting providers. After gaining access, the attackers exported device configurations via the GUI. These files include hashed credentials, which threat actors can attempt to crack offline, increasing the risk of further compromise.
Scientists Found a Real Mummy’s Curse Hiding in the Online Trade in Human Remains
The mummy of Ramses I. Credit: Wikimedia Commons Disturb the dead and…
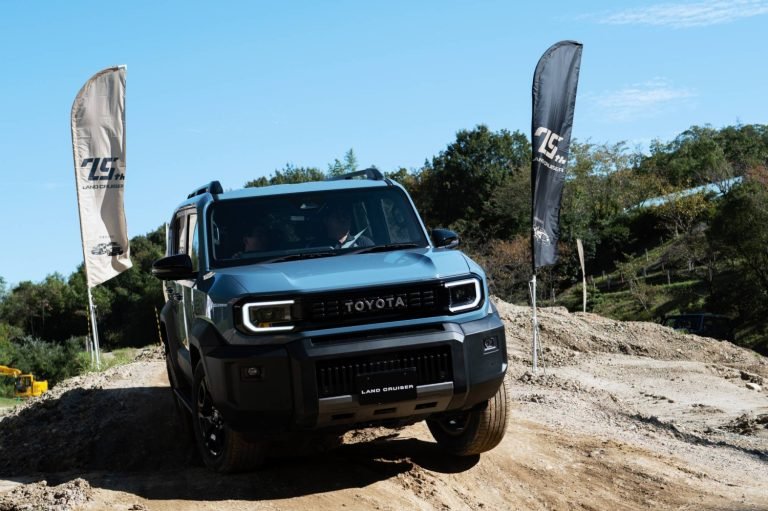
Toyota’s ‘baby’ Land Cruiser seen bolstering Asia car sales
Toyota Motor is counting on a new Land Cruiser, the smallest in…
Urgent Warning: Massive Train Disruptions Threaten Philly to NYC Commuters Today
PHILADELPHIA — For anyone planning a trip from the Delaware Valley up…
Rep. Perry Slams Washington Over High Stakes E15 Fuel Fight and Mandates
As Capitol Hill navigates a dense legislative calendar and rising pressures over…
Rep. Perry Unveils Major SURFACE Act Legislation in Crucial House Address
As Capitol Hill navigates a packed legislative calendar, lawmakers continue to introduce…
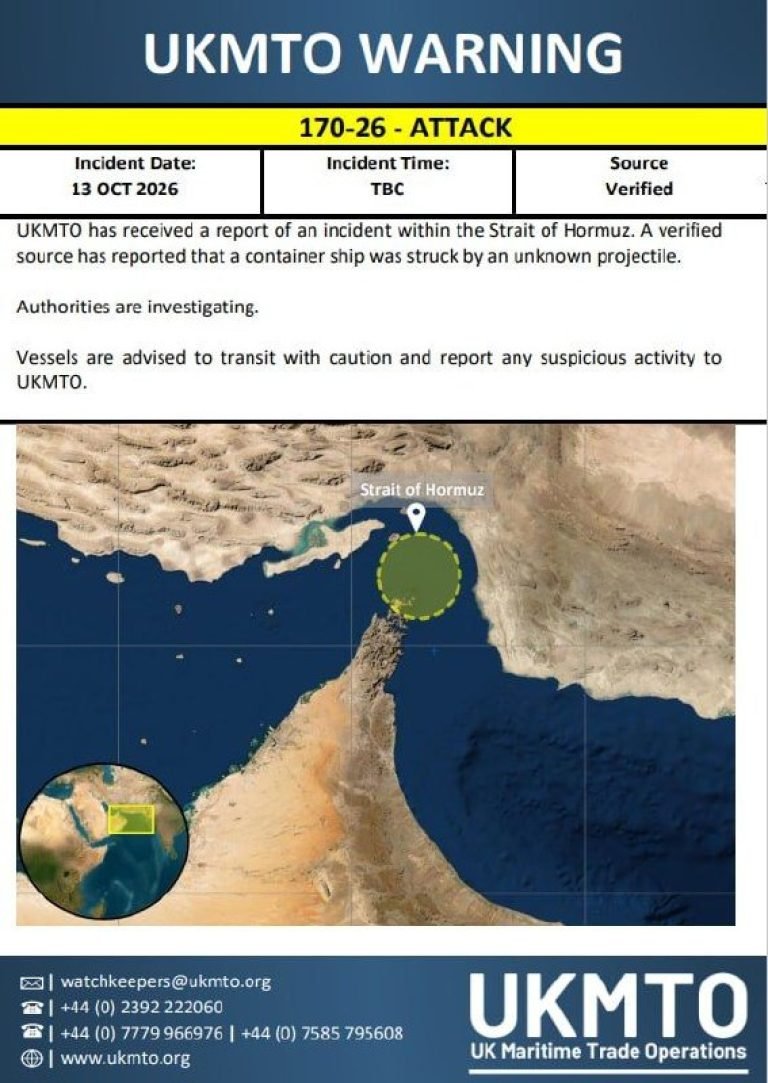
Strategic Assessment: Iranian Forces Target Two Violating Vessels Near Strategic Strait
STRATEGIC INTELLIGENCE UPDATE: SECURING THE WORLD'S ENERGY ARTERY Geopolitical tensions in the…
Recent intrusions show malicious SSO logins from a small set of hosting providers, often targeting the [email protected] account. After successful SSO access, attackers quickly exported firewall configurations via the GUI and created secondary admin accounts for persistence. These actions occurred within seconds, suggesting highly automated activity.
This week, Fortinet confirmed that attacks succeeded even against devices patched for CVE-2025-59718 and CVE-2025-59719.
The company identified a new attack path after observing login exploits on fully updated devices. A fix is in progress, an advisory is pending, and all SAML SSO implementations may be affected.
“Recently, a small number of customers reported unexpected login activity occurring on their devices, which appeared very similar to the previous issue. However, in the last 24 hours, we have identified a number of cases where the exploit was to a device that had been fully upgraded to the latest release at the time of the attack, which suggested a new attack path.” reads the advisory published by the company.
“Fortinet product security has identified the issue, and the company is working on a fix to remediate this occurrence. An advisory will be issued as the fix scope and timeline is available. It is important to note that while, at this time, only exploitation of FortiCloud SSO has been observed, this issue is applicable to all SAML SSO implementations.”
Fortinet is developing a fix, in the meantime, it released IOCs to aid threat hunting. Customers are urged to restrict admin access, limit it to local IPs, and temporarily disable FortiCloud SSO as a workaround.