

The U.S. Cybersecurity and Infrastructure Security Agency (CISA) adds a flaw in multiple Fortinet products to its Known Exploited Vulnerabilities catalog.
The U.S. Cybersecurity and Infrastructure Security Agency (CISA) added a Broadcom VMware vCenter Server vulnerability, tracked as CVE-2026-24858 (CVSS score of 9.4), to its Known Exploited Vulnerabilities (KEV) catalog.
This week, Fortinet started rolling out patches for a critical FortiOS flaw under active attack. The bug, CVE-2026-24858 (CVSS score of 9.4), lets attackers bypass authentication via SSO. It affects FortiOS, FortiManager, and FortiAnalyzer, while Fortinet checks if other products are impacted.
“An Authentication Bypass Using an Alternate Path or Channel vulnerability [CWE-288] in FortiOS, FortiManager, FortiAnalyzer may allow an attacker with a FortiCloud account and a registered device to log into other devices registered to other accounts, if FortiCloud SSO authentication is enabled on those devices.” reads the advisory. “Please note that the FortiCloud SSO login feature is not enabled in default factory settings. However, when an administrator registers the device to FortiCare from the device’s GUI, unless the administrator disables the toggle switch “Allow administrative login using FortiCloud SSO” in the registration page, FortiCloud SSO login is enabled upon registration.”
The company pointed out that FortiCloud SSO login is disabled by default. It only activates when an admin registers the device to FortiCare via the GUI or explicitly enables the FortiCloud SSO admin login option.
The cybersecurity vendor confirmed the flaw was exploited by two malicious FortiCloud accounts, blocked on Jan 22, 2026. To stop abuse, FortiCloud SSO was disabled on Jan 26, then re-enabled on Jan 27. SSO now blocks vulnerable versions, forcing customers to upgrade to supported releases to continue using FortiCloud SSO authentication.
The company is still investigating if other solutions, such as FortiWeb and FortiSwitch Manager are impacted by the vulnerability.
Maingear Instant Trade-In Program Maximizes Gaming PC Value and Hardware Upgrades
Maingear Launches Instant Trade-In Program for Gaming PC Buyers American custom and…
Dragon’s Dogma 2 Dark Arisen: The Ultimate Guide to DLC Changes, Prices, and Beginner Tips
Buying a game or expansion right before it unlocks can be an…
CAUGHT RED-HANDED: Federal Task Force Busts Massive $130M Los Angeles Homelessness Fraud Ring
LOS ANGELES, CA — In what is rapidly becoming one of the…
The U.S. said China was priming a trade superweapon. Then it vanished.
WENZHOU, CHINA/TOKYO – Four years ago, the United States warned that China…
APT28 exploits Microsoft Office flaw in Operation Neusploit
Russia-linked APT28 is behind Operation Neusploit, exploiting a newly disclosed Microsoft Office…
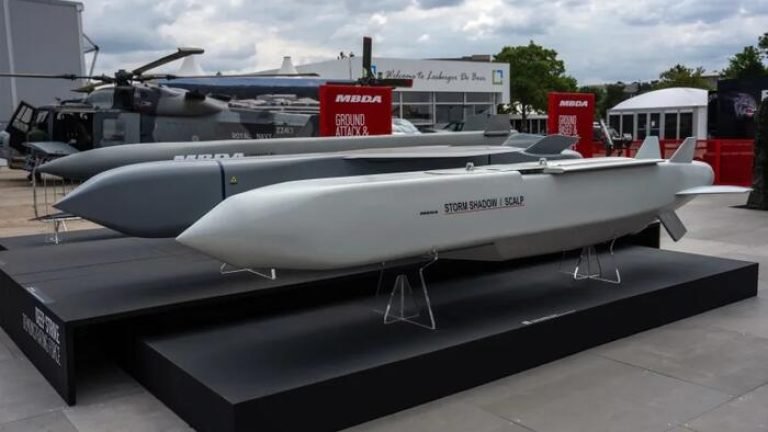
Moscow Warns It Could Target British Military Facilities In Unprecedented Statement
From the very start of the Ukraine war, the United Kingdom has…
Fortinet provided a workaround stating that FortiCloud SSO no longer allows logins from devices running vulnerable versions, so disabling SSO on the client side is not strictly required. However, as an extra precaution, administrators can manually disable FortiCloud SSO on FortiOS, FortiProxy, FortiManager, and FortiAnalyzer via the GUI or CLI until systems are fully patched.
According to Binding Operational Directive (BOD) 22-01: Reducing the Significant Risk of Known Exploited Vulnerabilities, FCEB agencies have to address the identified vulnerabilities by the due date to protect their networks against attacks exploiting the flaws in the catalog.
Experts also recommend that private organizations review the Catalog and address the vulnerabilities in their infrastructure.
CISA orders federal agencies to fix the vulnerability by January 30, 2026.
US CISA also published an alert related to this flaw titled “Fortinet Releases Guidance to Address Ongoing Exploitation of Authentication Bypass Vulnerability CVE-2026-24858“