

Huntress confirmed active SolarWinds Web Help Desk exploits, where attackers installed Zoho tools for persistence, and used Velociraptor for control.
On February 7, 2026, Huntress investigated an active attack abusing SolarWinds Web Help Desk flaws. Attackers exploited unpatched versions to run code remotely, then quickly installed Zoho ManageEngine tools for persistent remote access and Cloudflare tunnels.
“This intrusion stemmed from the many recently disclosed vulnerabilities affecting SolarWinds WHD. The most critical vulnerabilities grant an adversary arbitrary code execution via untrusted deserialization — CVE-2025-40551 was recently added to CISA’s Known Exploited Vulnerabilities database, and CVE-2025-26399 was just recently discussed by Microsoft and other vendors who have also observed active in-the-wild exploitation.” reads the report published by Huntress. “They used Velociraptor to control systems and ran domain discovery commands to map networks. The activity confirms real-world exploitation of critical SolarWinds WHD vulnerabilities now tracked by CISA.”
Huntress observed active post-exploitation after attackers compromised SolarWinds Web Help Desk. The attack started from the WHD service, which silently installed a Zoho ManageEngine RMM agent to gain persistent remote access.
“Interestingly, the Zoho Assist agent was configured for unattended access, registering the compromised host to a Zoho Assist account tied to a Proton Mail address, esmahyft@proton[.]me.” continues the report. “Once the Zoho ManageEngine RMM agent was established, the threat actor wasted no time pivoting to hands-on-keyboard activity. Using the RMM agent process (TOOLSIQ.EXE) as their operational foothold, they executed Active Directory discovery commands to enumerate domain-joined machines via net group "domain computers" /do, a textbook reconnaissance technique aimed at identifying viable targets for lateral movement.”
Russia Hits Kiev Ammo Dump Next To Homes; Ukraine Admits 90% Of Retail Food Logistics Wrecked
A Russian drone struck a Ukrainian Defense Forces ammunition storage site in…
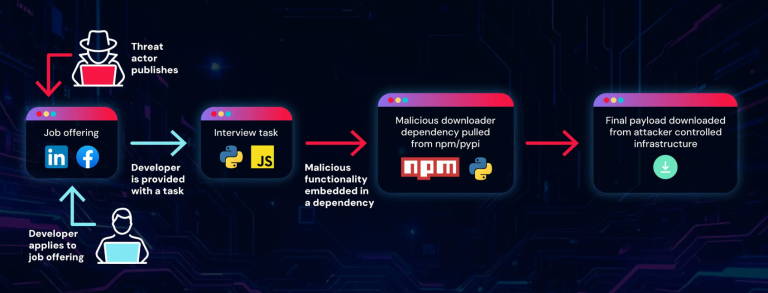
Malicious npm and PyPI packages linked to Lazarus APT fake recruiter campaign
Researchers found malicious npm and PyPI packages tied to a fake recruitment…
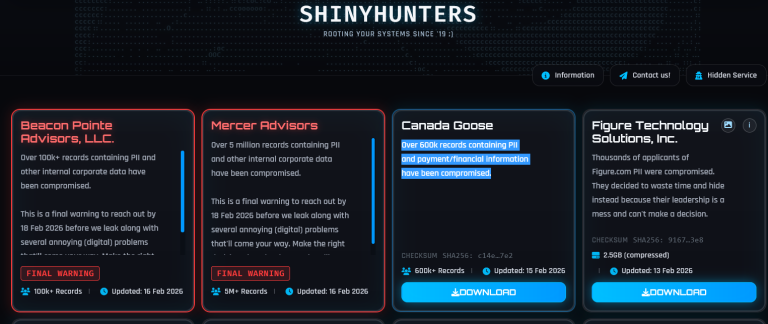
ShinyHunters leaked 600K+ Canada Goose customer records, but the firm denies it was breached
ShinyHunters leaked 600,000+ Canada Goose customer records, though the company insists its…
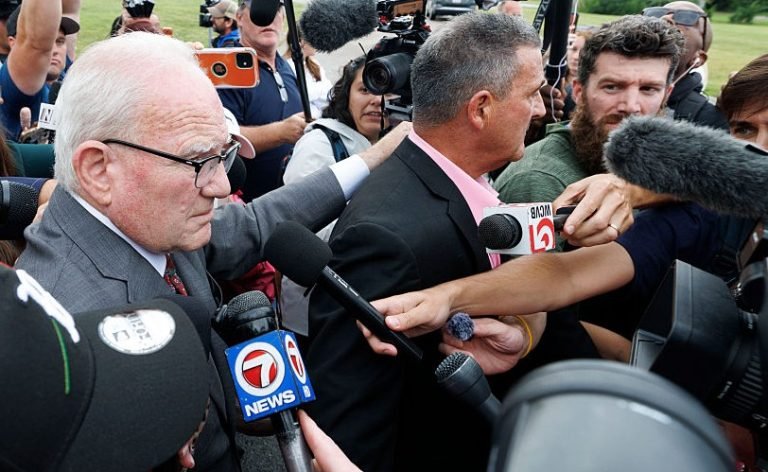
BREAKING: Lindsay Clancy mistrial declared after male juror holds out
The Lindsay Clancy murder trial stumbled toward a mistrial declaration today as…
Simply Sniffing Dark Chocolate Helped Men Squeeze Out 18 More Reps in the Gym During Leg Day
Credit: Unsplash. Could the smell of chocolate wafting through the gym make…
2,000 Pairs of Underwear Were Turned Into a Giant Soil Experiment and the Results Were Surprisingly Revealing
Slightly or heavily decomposed? The more active the soil organisms, the faster…
Using this foothold, the attacker performed domain reconnaissance, then deployed Velociraptor as a command-and-control tool. Velociraptor was configured to communicate through Cloudflare Workers and included a failover C2 mechanism.
The attacker quickly ran a PowerShell script to collect detailed system information, including OS details, hardware data, domain membership, and installed updates. This data was formatted and sent to an attacker-controlled Elastic Cloud instance hosted on legitimate Google Cloud infrastructure, effectively giving the attacker a centralized dashboard to track and manage compromised systems using Kibana.
To avoid detection, they disabled Windows Defender and the Windows Firewall. They then installed Cloudflared tunnels to maintain hidden remote access and used PowerShell to execute additional commands and manage the system. To ensure long-term persistence, the attacker also created malicious scheduled tasks that abused QEMU to keep access even after reboots.
Below are mitigations provided by the Huntress, along with Indicators of Compromise (IoCs):
- Update SolarWinds Web Help Desk to version 2026.1 or later, which addresses CVE-2025-26399, CVE-2025-40536, and CVE-2025-40551. All prior versions should be considered vulnerable. See the SolarWinds upgrade guide for instructions.
- WHD administrative interfaces should not be publicly accessible. Place WHD behind a VPN or firewall and remove direct internet access to admin paths.
- Reset passwords for all service accounts, administrator accounts, and any credentials accessible through or stored within the WHD application.
- Review WHD hosts for unauthorized remote access tools (Zoho Assist, Velociraptor, Cloudflared, VS Code tunnels), unexpected services, encoded PowerShell execution, and silent MSI installations spawned by the WHD service process (java.exe / wrapper.exe).