

Dutch agencies confirmed attacks exploiting Ivanti EPMM flaws that exposed employee contact data at the data protection authority and courts.
Dutch authorities said cyberattacks hit the Dutch Data Protection Authority and the Council for the Judiciary after hackers exploited newly disclosed flaws in Ivanti Endpoint Manager Mobile (EPMM). The incidents were reported to parliament, and the National Cyber Security Center was alerted on January 29 after the vendor disclosed the vulnerabilities. EPMM manages mobile devices, apps, and security, and the attacks exposed employee contact information.
“State Secretary Rutte (JenV) and State Secretary Van Marum (BZK) informed the House of Representatives about the exploitation of a vulnerability in Ivanti Endpoint Manager Mobile (EPMM) at the Dutch Data Protection Authority (AP) and the Judicial Council (Rvdr). EPMM is a system for managing mobile devices, apps, and content, including their security.” reads the advisory. “On 29 January the National Cyber Security Centre (NCSC) was informed by the supplier of vulnerabilities in EPMM. EPMM is used to manage mobile devices, apps and content, including their security. Based on the information known at this moment, I can report that at least the AP and the Rvdr have been affected. “
Attackers accessed work-related contact details of AP staff, including names, work emails, and phone numbers. Authorities quickly took action, informed affected employees, and reported the incident. The NCSC continues to monitor the issue and assess any wider impact across government systems.
“It is now known that work‑related data of AP employees, such as name, business e‑mail address and telephone number, have been accessed by unauthorised parties.” continues the advisory. “As soon as the incident was discovered, measures were taken immediately. In addition, the employees of the AP and the Rvdr were informed.”
Ancient Colombians Built a Landscape Bigger Than London Without Needing a Ruler
Satellite imagery of northern Colombia’s wetlands revealed an extraordinary human experiment: thousands…
BREAKING: Lindsay Clancy mistrial declared after male juror holds out
The Lindsay Clancy murder trial stumbled toward a mistrial declaration today as…
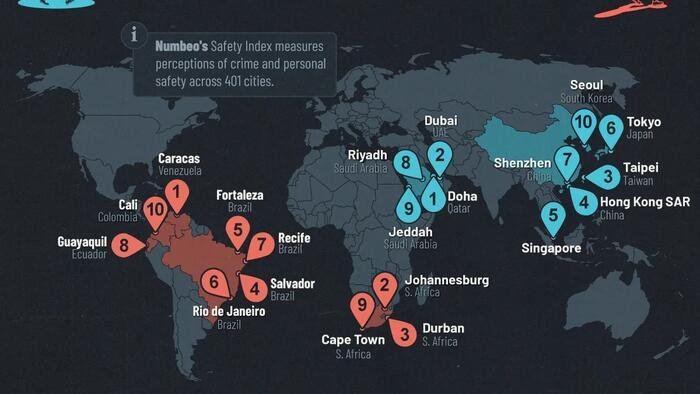
These Are The World's Safest (And Least Safe) Cities
Doha ranks as the safest major city in the world in 2026,…
Naomi Wolf Crashes Out on ‘The Alex Jones Show’ Over October 7 stand-down Claims
An explosive debate erupted today on The Alex Jones Show when guest…
The Songwriter Who Taught America How to Love: Remembering Dolly Parton
There are rare figures in American culture who do not merely occupy…
First Secondary Sanctions Applied: US Blocks Egyptian Bank From Accessing Dollars Over 'Iran Ties'
The US Treasury Department on Friday unveiled its first 'secondary' Iran sanctions…
This week, the European Commission announced it is investigating a cyberattack on its mobile device management platform after detecting intrusion traces. Attackers may have accessed some staff data, including names and phone numbers, but so far they have not compromised any devices.
On 30 January, the European Commission detected a cyberattack on its mobile device management system. The organization pointed out that no mobile devices were compromised. The Commission contained and cleaned the system within nine hours. It continues to monitor security, strengthen cybersecurity, and review the incident to improve protections, reflecting its commitment to safeguarding EU systems amid ongoing cyber threats to critical services and institutions.
“On 30 January, the European Commission’s central infrastructure managing mobile devices identified traces of a cyber-attack, which may have resulted in access to staff names and mobile numbers of some of its staff members.” reads the advisory. “The Commission’s swift response ensured the incident was contained and the system cleaned within 9 hours. No compromise of mobile devices was detected.”
The Commission has not revealed how the threat actors accessed the mobile device management platform.
The European Computer Emergency Response Team (CERT-EU) is investigating the security breach.
Attackers could use the stolen data to launch targeted vishing and phishing attacks by impersonating colleagues or officials to steal credentials. The stolen data enables reconnaissance for spear phishing or physical targeting of key personnel. Finally, GDPR violations and reputational damage undermine the Union’s cyber credibility.