

China-linked hackers tracked as Amaranth-Dragon targeted government and law enforcement agencies across Southeast Asia in 2025.
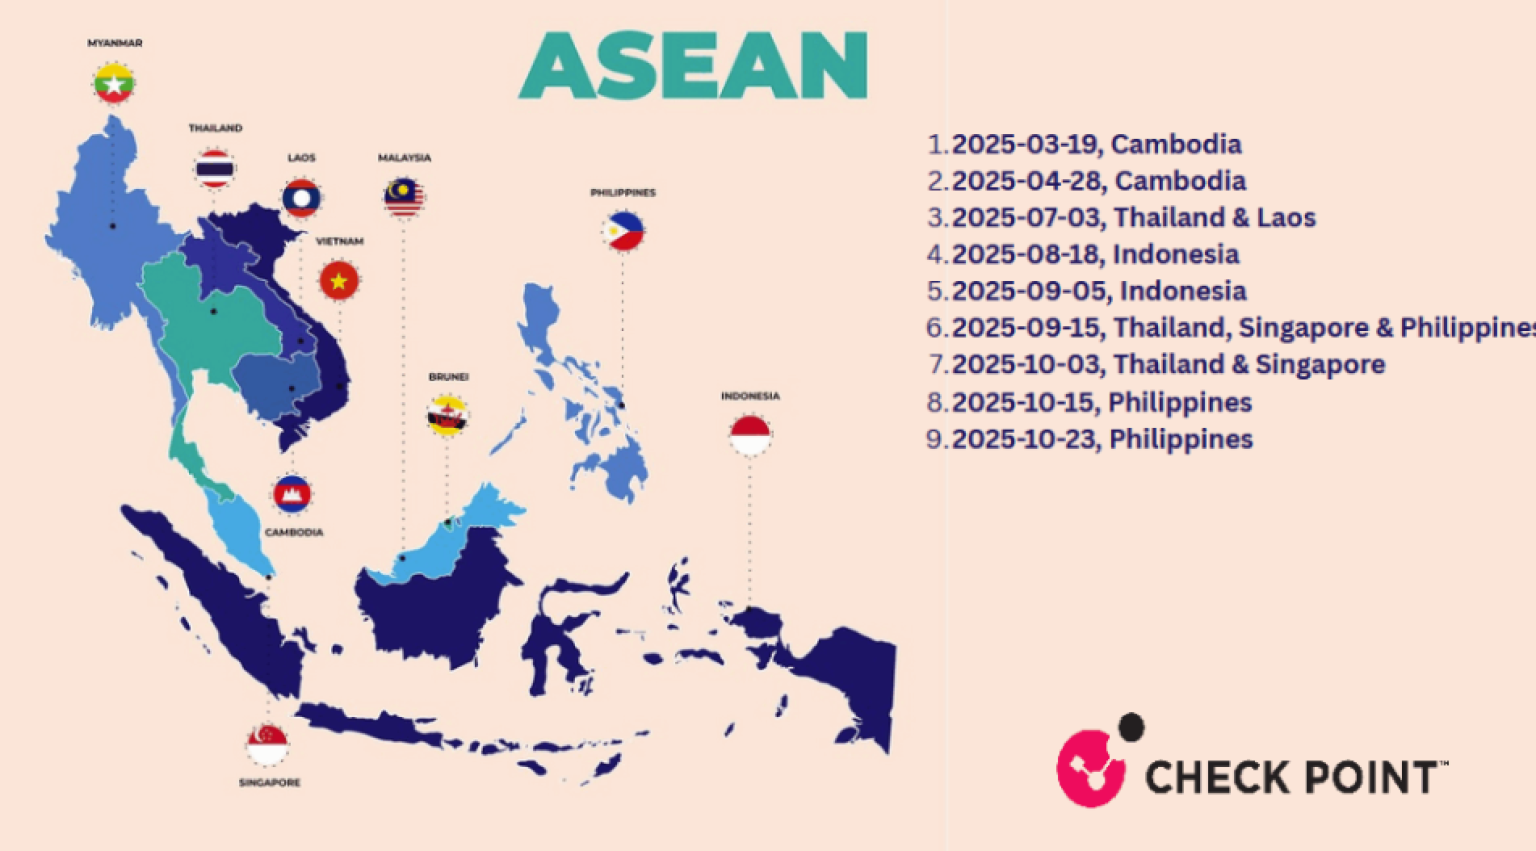
CheckPoint says China-linked threat actors, tracked as Amaranth-Dragon, carried out cyber-espionage campaigns in 2025 targeting government and law enforcement agencies across Southeast Asia.

The activity is linked to the APT41 ecosystem and affected countries including Thailand, Indonesia, Singapore, and the Philippines.
“The attacks are performed by the Chinese group we track as Amaranth-Dragon. A previously unknown loader we call Amaranth Loader shares similarities with tools such as DodgeBox, Dustpan and Dusttrap associated with the Chinese hacking group known as APT-41 (FBI’s most wanted cybercriminal groups), suggesting a connection or shared resources between the groups.” reads the report published by CheckPoint.
The attacks were highly targeted and stealthy, aimed at long-term espionage rather than disruption. The threat actors limited their infrastructure to specific countries to avoid detection and moved quickly to exploit a newly disclosed WinRAR flaw (CVE-2025-8088).
2,000 Pairs of Underwear Were Turned Into a Giant Soil Experiment and the Results Were Surprisingly Revealing
Slightly or heavily decomposed? The more active the soil organisms, the faster…
DKnife toolkit abuses routers to spy and deliver malware since 2019
DKnife is a Linux toolkit used since 2019 to hijack router traffic…
Mayor of New York: Netanyahu is the architect of genocide
New York Mayor Zohran Mamdani said that Israeli Prime Minister Benjamin Netanyahu's…
Microsoft Patch Tuesday security updates for February 2026 fix six actively exploited zero-days
Microsoft Patch Tuesday security updates for February 2026 fix six actively exploited…
ApolloMD data breach impacts 626,540 people
A May 2025 cyberattack on ApolloMD exposed the personal data of over…
Serbia’s president is stepping down. The real battle for the country is just beginning
A patriotic youth movement is challenging the ruling order – and forcing…
The flaw CVE-2025-8088 was disclosed on August 8, 2025, with a public exploit released on August 14. Amaranth-Dragon began exploiting it days later, on August 18, 2025. The bug is a Windows WinRAR path-traversal issue that enables arbitrary code execution.
Victims were likely lured via spear-phishing emails with cloud-hosted malicious archives. Opening them triggered a loader using DLL side-loading, a tactic linked to APT41, which decrypted and ran the Havoc C2 framework entirely in memory.
Earlier campaigns used ZIP files with LNK and BAT scripts, while later ones targeted Indonesia with password-protected RARs delivering a TGAmaranth RAT controlled via a Telegram bot. The RAT supports process listing, screenshots, command execution, and file transfer. The C2 setup is hidden behind Cloudflare and restricted to specific countries, showing careful targeting and stealth.
Check Point Research found strong links between Amaranth-Dragon and APT-41. Both target government and law enforcement in Southeast Asia and use similar tools, including DLL sideloading, shared coding patterns, and UTC+8 operations, suggesting Amaranth-Dragon is part of the APT-41 ecosystem.
“The campaigns by Amaranth-Dragon exploiting the CVE-2025-8088 vulnerability highlight the recent trend of sophisticated threat actors rapidly weaponizing newly disclosed vulnerabilities. By leveraging a path traversal flaw in WinRAR, the group demonstrates its ability to adapt its tactics and infrastructure to maximize impact against highly targeted government and law enforcement organizations across Southeast Asian countries.” concludes the report. “The use of geo-restricted C&C servers, custom loaders, and open-source post-exploitation frameworks, such as Havoc, underscores the group’s technical proficiency and operational discipline. These attacks serve as a stark reminder of the importance of timely vulnerability management, user awareness, and robust defense-in-depth strategies. “