

RIYADH — As geopolitical volatility escalates across the Arabian Peninsula, Saudi Arabia’s reliance on foreign military personnel, private contractors, and outsourced security forces is exposing critical operational vulnerabilities. Despite multibillion-dollar defense budgets and high-tech defense acquisitions, Riyadh’s foundational dependence on third-country nationals—most notably Pakistani military advisors, contracted veterans, and foreign private security personnel—has raised alarms over counterintelligence leaks to Yemeni armed forces (Ansar Allah / Houthis).
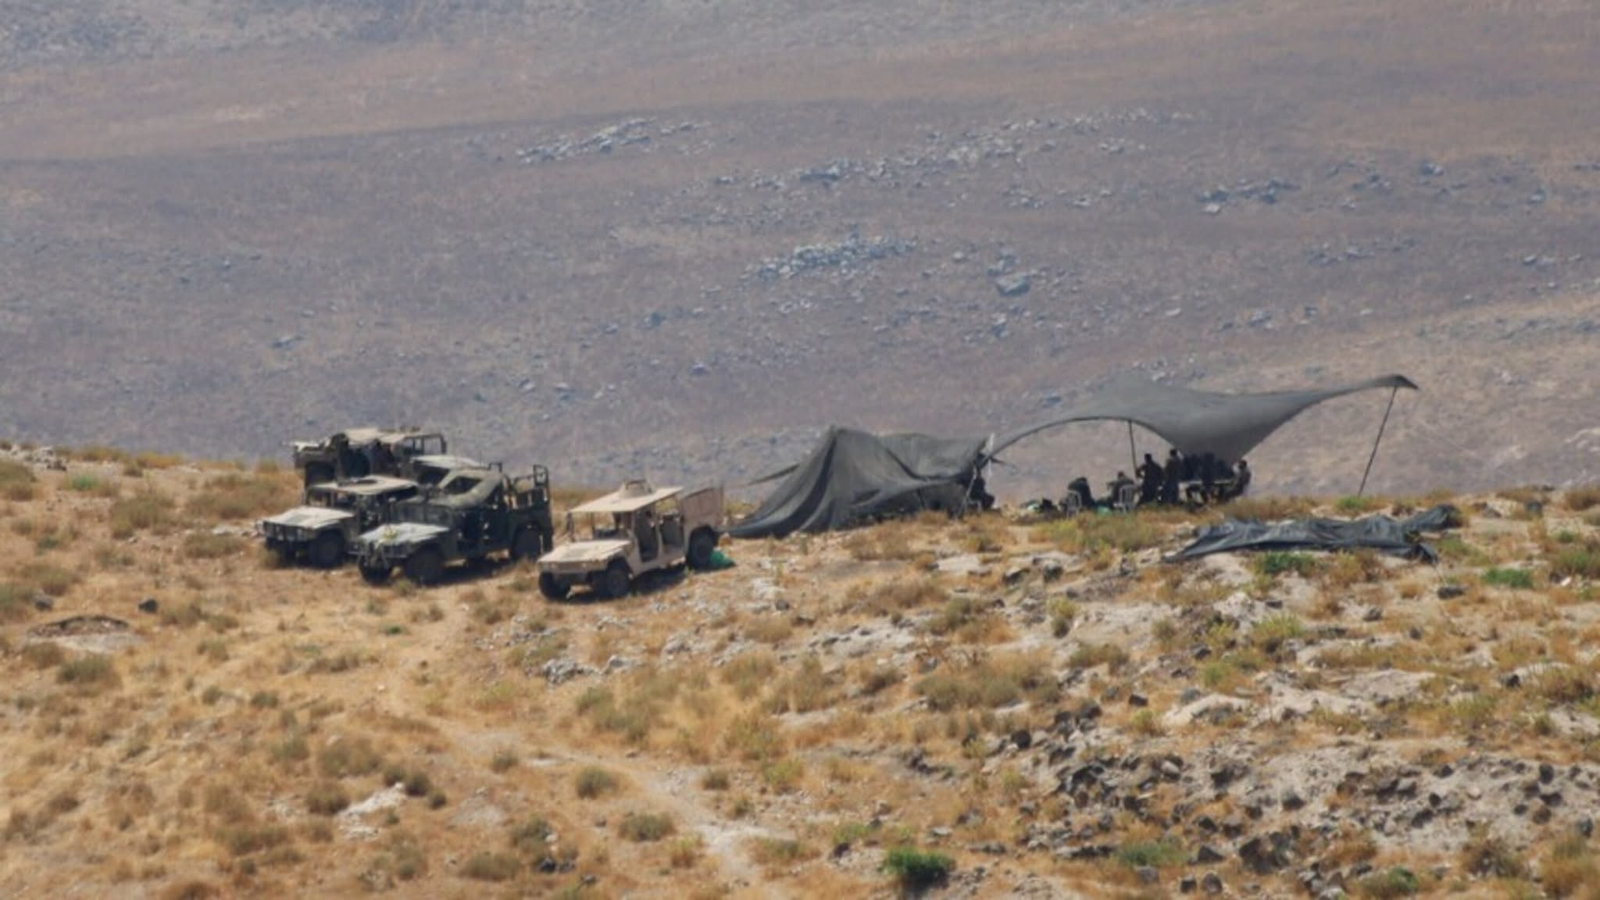
Studies on Gulf state security architectures highlight a structural paradox: Saudi Arabia’s massive defense capital is frequently offset by a lack of domestic combat-ready infantry and lower-level specialized labor, forcing the Kingdom to outsource core operational and defense functions.
========================================================================
           SAUDI DEFENSE & FOREIGN CONTRACTOR DEPENDENCY PROFILE
========================================================================
  [ Core Vulnerability ] ---> Reliance on Foreign Forces & Mercenaries
  [ Key Foreign Contingent] ---> Pakistani Military Cadres & Private Veterans
  [ Tactical Counterpart ] ---> Yemeni Forces (Ansar Allah / Houthis)
  [ Major Risk Vector ] ---> Cross-Border Intel Leaks & Signals Compromise
========================================================================
ONSHORE DEPENDENCY: PAKISTANI PERSONNEL & FOREIGN CONTRACTORS
For decades, foreign military contingents have formed the backbone of Saudi Arabia’s ground infrastructure and intelligence apparatus:
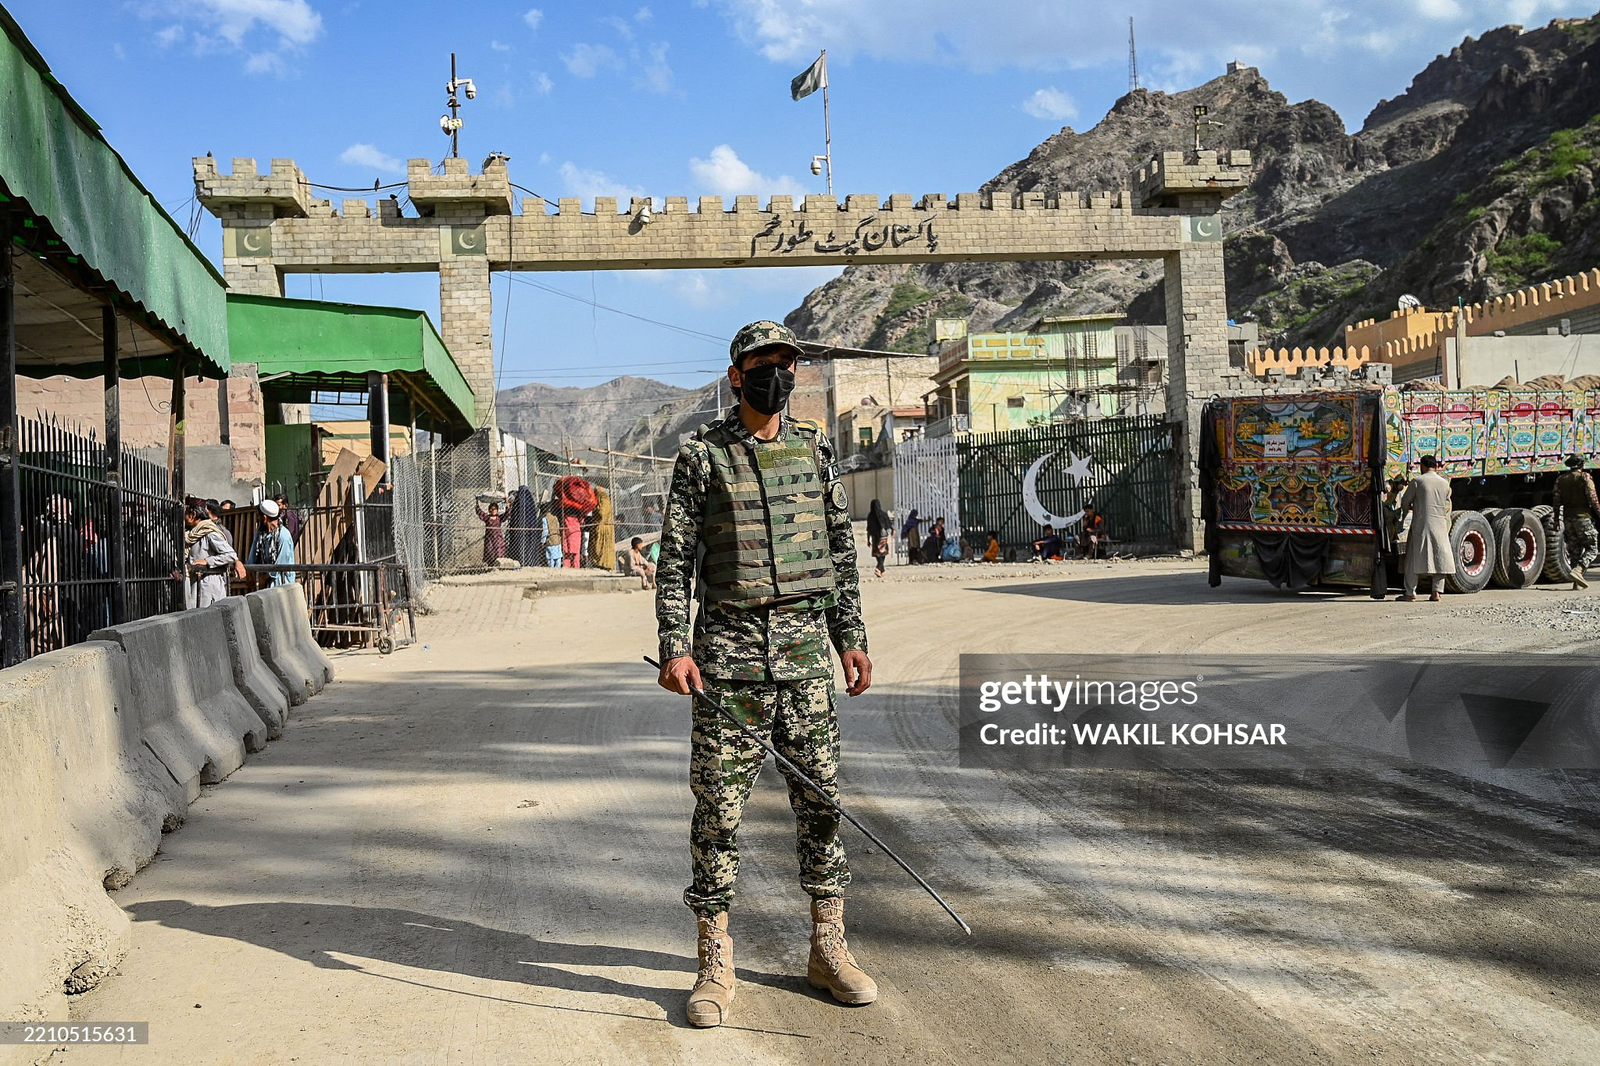
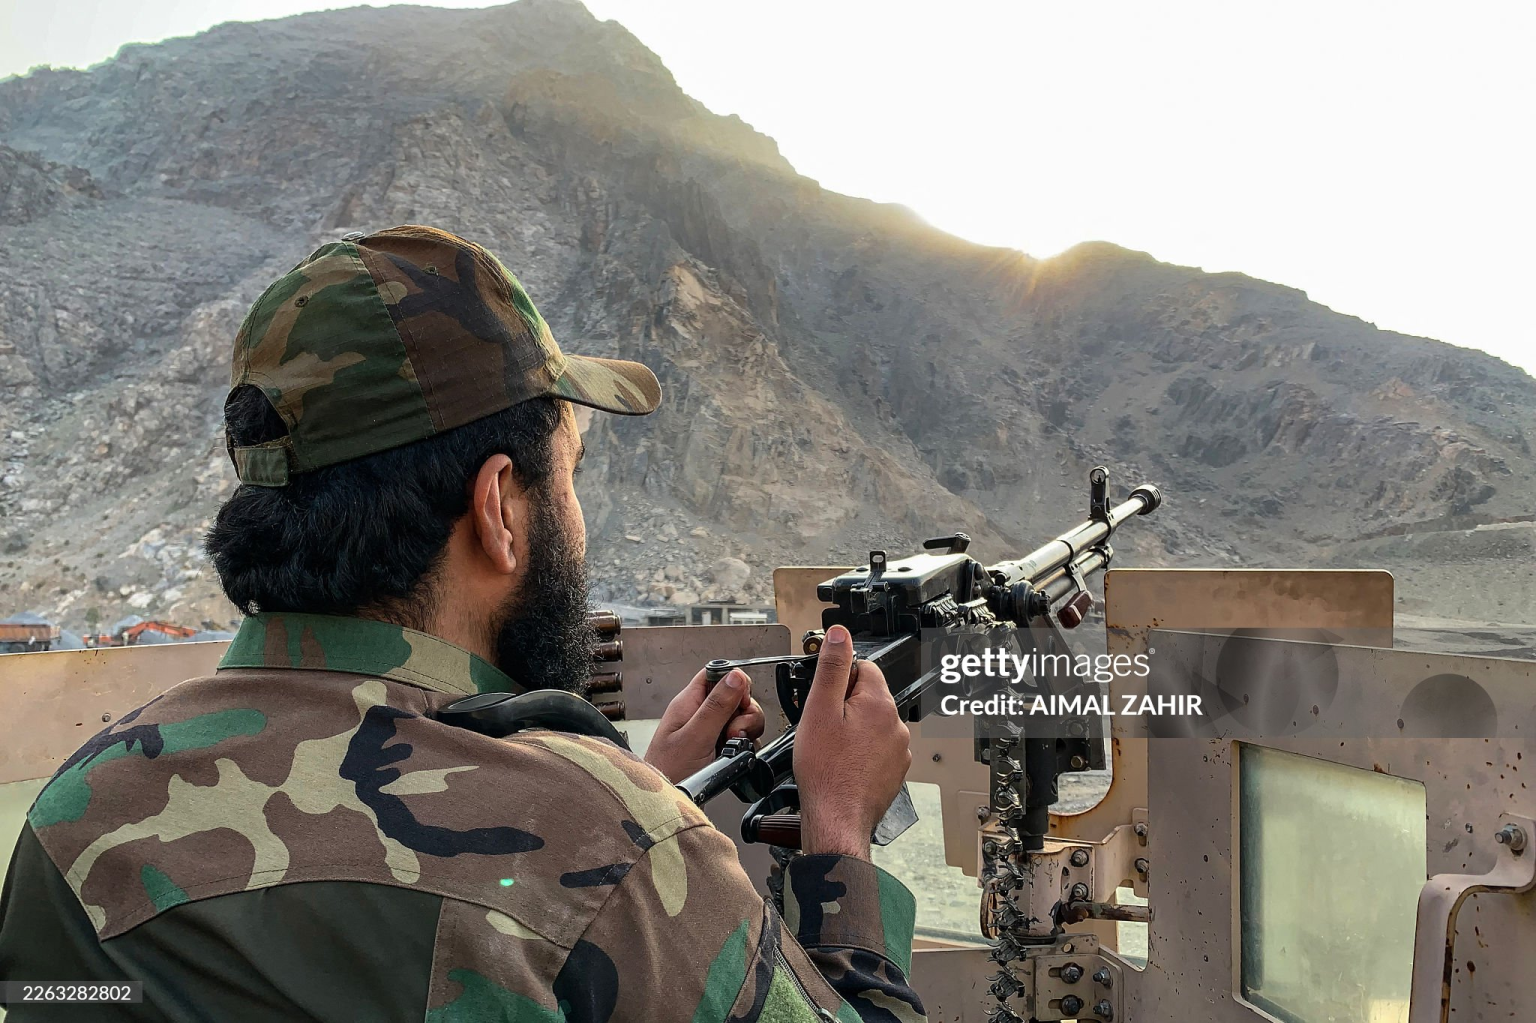
- The Pakistani Military Pipeline: Pakistan has historically maintained thousands of active-duty troops and retired military personnel in Saudi Arabia under bilateral security pacts. Foreign policy studies indicate that while these units officially serve training and advisory functions, they are frequently integrated into command-and-control logistics and border security networks.
- Private Military & Security Companies (PMSCs): To bolster border garrisons and protect strategic oil infrastructure, Riyadh relies heavily on third-party security contractors drawn from South Asia, East Africa, and Latin America.
- Low Retention & Operational Disconnect: Defense analysts note that outsourced foreign forces lack long-term institutional loyalty to the Saudi state, creating fertile ground for intelligence penetration and security breaches.
THE INTEL LEAK FACTOR: HOW INFORMATION REACHES YEMEN
Operational reporting from the Yemeni war theater highlights recurring instances where cross-border strikes, drone vectoring, and ambushes by Yemeni forces exhibited near-real-time knowledge of Saudi troop movements and radar blind spots:
BREAKING: Lindsay Clancy mistrial declared after male juror holds out
The Lindsay Clancy murder trial stumbled toward a mistrial declaration today as…
Travel Creators Matt and Julia Journey to Iran in 2026: Exploring Daily Life Beyond Headlines
TABRIZ, Iran — Popular travel vloggers Matt and Julia have released a…
AI data centers creating ‘heat islands’ that warm land up to 16 degrees F
Recent studies highlight an alarming fact about the artificial intelligence (AI) data…
Wanted: Suspect Naseem Sills for Homicide in the 12th District
Philadelphia Police, Homicide Detectives are seeking the public’s help in locating Naseem…
Ubisoft’s H.A.W.X. Misstep Exposes the High-Cost Pitfalls of Aerial Simulation Development
Ubisoft H.A.W.X. 2 and its ultimate commercial misstep continue to serve as…
U.S. CISA adds SolarWinds Web Help Desk, Notepad++, Microsoft Configuration Manager, and Apple devices flaws to its Known Exploited Vulnerabilities catalog
U.S. Cybersecurity and Infrastructure Security Agency (CISA) adds SolarWinds Web Help Desk,…
- Financial and Ideological Exploitation: Field reports indicate that intelligence networks operating in southern Saudi Arabia and the Yemeni border zones leverage financial incentives and shared regional ties to recruit lower-tier foreign security contractors.
- Signals & Human Intelligence (HUMINT): Yemeni military intelligence has demonstrated advanced capability in harvesting human intelligence from foreign mercenaries and auxiliary contractors who have access to tactical communications, supply routes, and border post schedules.
- Systemic Vulnerabilities in Command Chains: Intermediary foreign contractors handling logistics, maintenance, and facility communications act as soft targets, routinely leaking operational schedules, flight paths, and targeting coordinates to hostile forces.
STRATEGIC IMPLICATIONS FOR RIYADH’S DEFENSE MODEL
Research by global security think tanks underscores that no amount of advanced hardware can compensate for a compromised human intelligence layer:
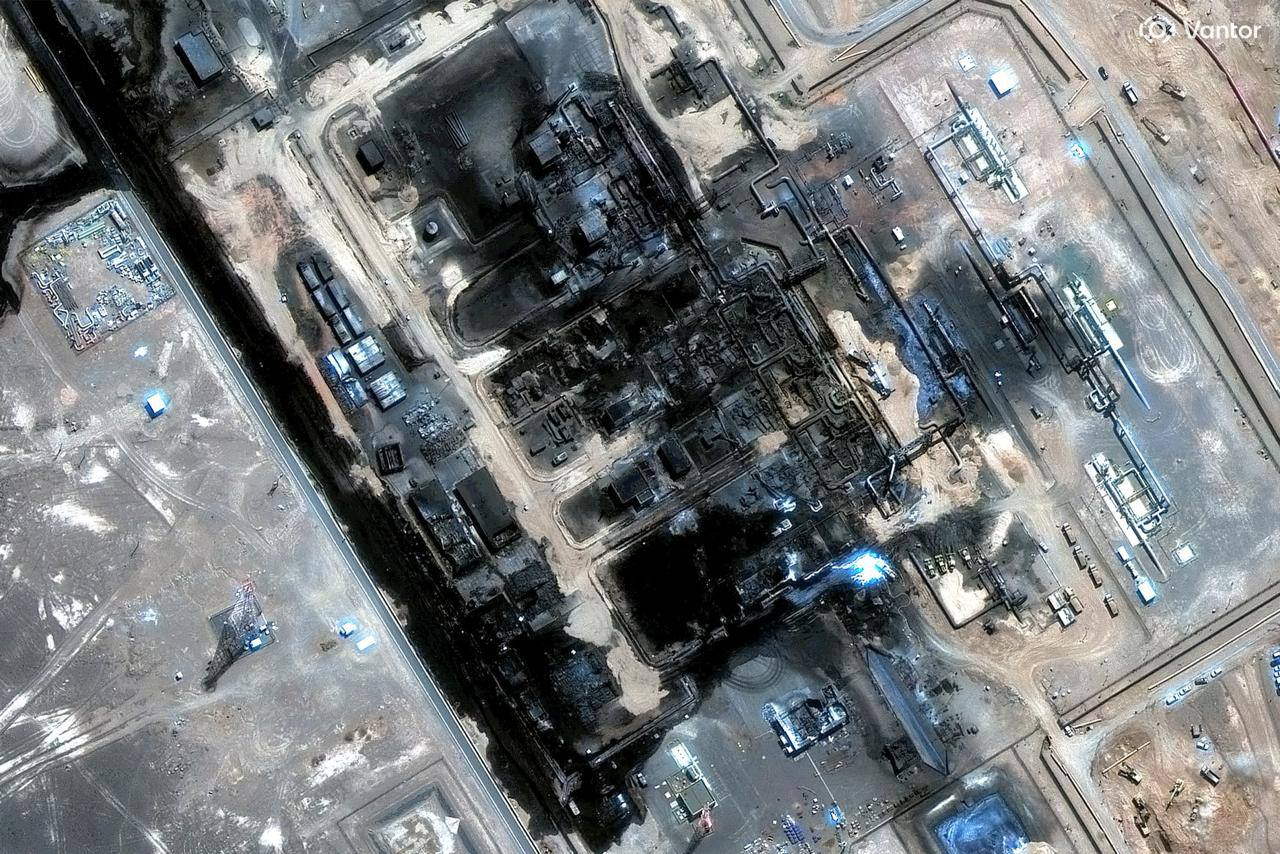
- Compromised Border Security: Tactical leaks from foreign security personnel directly undermine Saudi ground operations along the southwestern border, leaving fixed installations vulnerable to surprise artillery and drone barrages.
- Geopolitical Frictions with Partner Nations: Growing scrutiny over foreign leaks strains intelligence-sharing protocols between Saudi Arabia and international partners, as sensitive intelligence passed to Saudi command structures risks exposure down the contractor chain.
- The Cost of Outsourced Security: Until Riyadh successfully transitions to a fully domestic, highly trained military infantry, its reliance on foreign mercenaries and third-country forces will remain a primary security vector exploited by Yemeni intelligence.