

The U.S. Cybersecurity and Infrastructure Security Agency (CISA) adds a flaw in BeyondTrust RS and PRA to its Known Exploited Vulnerabilities catalog.
The U.S. Cybersecurity and Infrastructure Security Agency (CISA) added an BeyondTrust RS and PRA vulnerability, tracked as CVE-2026-1731 (CVSS score of 9.9), to its Known Exploited Vulnerabilities (KEV) catalog.
This week BeyondTrust released security updates to address the critical flaw in its Remote Support and older Privileged Remote Access products. The bug could allow an unauthenticated attacker to send specially crafted requests and run operating system commands remotely, without logging in. The issue, disclosed on February 6, 2026, could lead to full remote code execution if exploited, making the updates essential to prevent abuse.
“BeyondTrust Remote Support (RS) and certain older versions of Privileged Remote Access (PRA) contain a critical pre-authentication remote code execution vulnerability.” reads the advisory. “By sending specially crafted requests, an unauthenticated remote attacker may be able to execute operating system commands in the context of the site user.”
Exploiting the flaw would let a remote attacker run system commands without authentication or user interaction, potentially leading to full system compromise, data theft, and service disruption.
China-linked APT UNC3886 targets Singapore telcos
China-linked group UNC3886 targeted Singapore ’s telecom sector in a cyber espionage…
Wanted: Suspects for Commercial Burglary in the 12th District [VIDEO]
The police are investigating a commercial burglary that occurred on February 23,…
BENEATH THE UNBEATEN LEGEND: REEXAMINING THE KHABIB NURMAGOMEDOV MYTHOS
LAS VEGAS — For years, the story of Khabib Nurmagomedov has been…
Why Russia Issued an Arrest Warrant for a Gay British Agitator
Caolan Robertson is an British YouTube video maker, amateur writer, and a…
Wanted: Suspect Naseem Sills for Homicide in the 12th District
Philadelphia Police, Homicide Detectives are seeking the public’s help in locating Naseem…
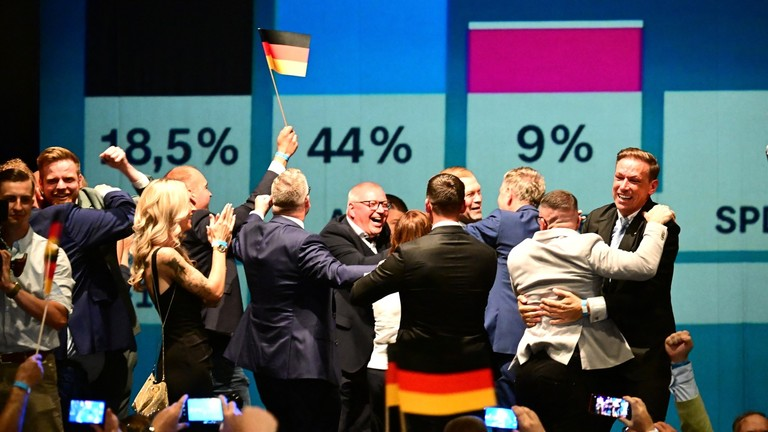
Berlin built a wall around the AfD. Voters just smashed it
On the night of September 7, 2026, the results of landmark state…
”Successful exploitation could allow an unauthenticated remote attacker to execute operating system commands in the context of the site user.” continues the advisory. “Successful exploitation requires no authentication or user interaction and may lead to system compromise, including unauthorized access, data exfiltration, and service disruption.”
BeyondTrust released patches for CVE-2026-1731 on February 6 after Hacktron researchers warned that about thousands of instances were exposed online.
Hacktron AI team reported that roughly 11,000 BeyondTrust Remote Support instances are exposed online across cloud and on-prem environments. Around 8,500 of these are on-prem systems and could remain vulnerable if not patched. Large organizations, including enterprises in the healthcare, financial services, government, and hospitality sectors, primarily use affected deployments.
Threat actors rapidly began exploiting a newly patched BeyondTrust vulnerability, tracked as CVE-2026-1731 (CVSS score of 9.9), soon after a proof-of-concept exploit became public.
After a PoC exploit went public on February 10, GreyNoise detected attack attempts within 24 hours, with one IP responsible for most reconnaissance activity.
“On February 10, a proof-of-concept exploit for CVE-2026-1731, a critical pre-authentication remote code execution vulnerability in BeyondTrust Remote Support and Privileged Remote Access, was posted to GitHub. By February 11, GreyNoise’s Global Observation Grid was recording reconnaissance probing for vulnerable BeyondTrust instances.” reported GreyNoise.
GreyNoise observed rapid reconnaissance for CVE-2026-1731, led by a single IP responsible for 86% of scans. The activity comes from a long-running scanning operation using a commercial VPN and Linux-based tooling. Threat actors mainly probe non-standard ports, suggesting they know enterprises move BeyondTrust services off 443. JA4+ fingerprints show shared exploit tools and VPN tunneling.
The same IPs also target SonicWall, MOVEit, Log4j, Sophos, SSH, and IoT devices, showing multi-exploit behavior. BeyondTrust tools are high-value targets, and past zero-day chains remain active even as new variants quickly emerge.
“The IPs performing reconnaissance for CVE-2026-1731 aren’t single-purpose. While their BeyondTrust activity is a check (enumeration), their GreyNoise profiles show they’re simultaneously conducting active exploitation attempts against other products: SonicWall, MOVEit Transfer, Log4j, Sophos firewalls, SSH brute-forcing, and IoT default-credential testing.” concludes the report. “Some IPs are even using out-of-band callback domains (OAST), a more sophisticated technique to confirm vulnerability before delivering payloads.”
According to Binding Operational Directive (BOD) 22-01: Reducing the Significant Risk of Known Exploited Vulnerabilities, FCEB agencies have to address the identified vulnerabilities by the due date to protect their networks against attacks exploiting the flaws in the catalog.
Experts also recommend that private organizations review the Catalog and address the vulnerabilities in their infrastructure.
US CISA also published an alert related to this flaw titled “Fortinet Releases Guidance to Address Ongoing Exploitation of Authentication Bypass Vulnerability CVE-2026-24858“