

Microsoft warns of a multi-stage phishing and BEC campaign hitting energy firms, abusing SharePoint links and inbox rules to steal credentials.
Microsoft reports an active multi-stage phishing campaign targeting energy sector organizations.
The campaign misused SharePoint file-sharing to deliver phishing links and created inbox rules to hide malicious activity and maintain persistence. After the initial compromise, attackers launched AiTM attacks that led to business email compromise across multiple organizations. They then abused trusted internal accounts to spread phishing internally and externally, expanding the attack’s reach. The activity highlights the complexity of AiTM campaigns and shows that effective remediation requires revoking active sessions and removing malicious inbox rules, not just resetting passwords.
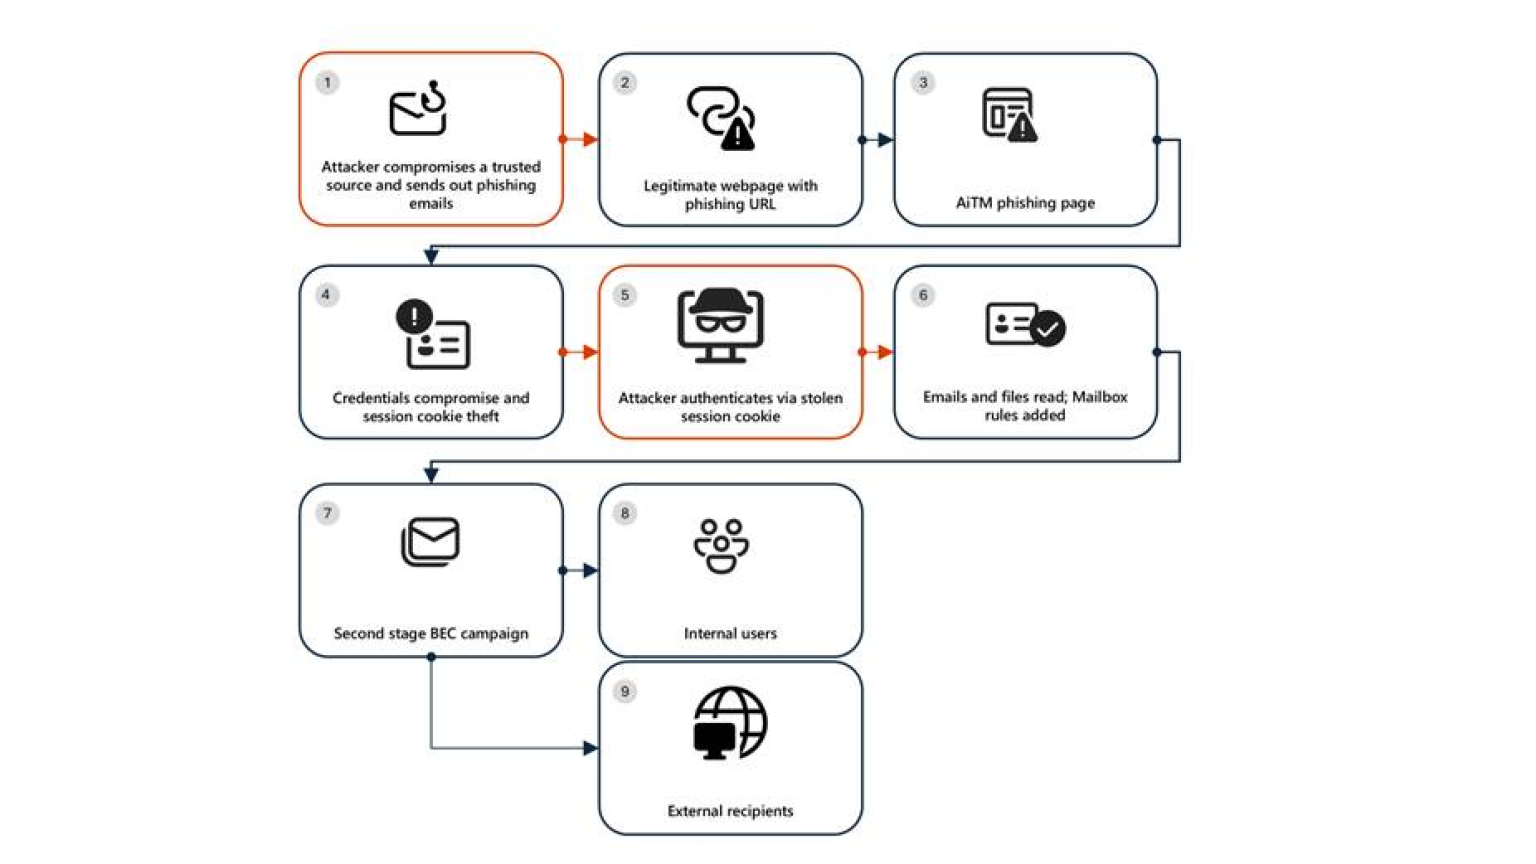
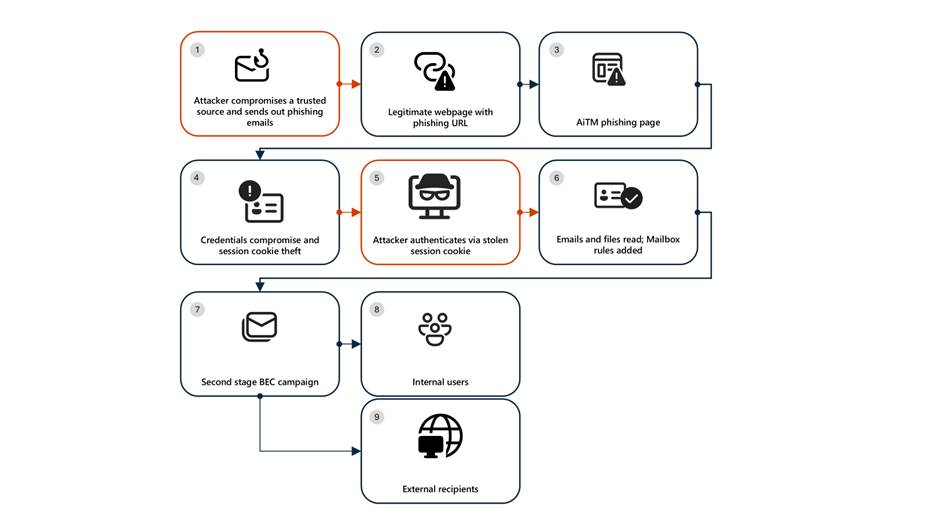
Below is the attack chain observed by Microsoft in the AiTM phishing campaign:
- Stage 1 – Initial access (trusted sender)
Attackers sent a phishing email from a compromised trusted organization. The message used a SharePoint link and realistic document-sharing subjects to appear legitimate. - Stage 2 – Malicious link click
Victims clicked the SharePoint URL. Attackers abused trusted cloud services like SharePoint to bypass email defenses. - Stage 3 – AiTM credential theft
The link redirected users to a fake sign-in page designed to steal credentials and session data. - Stage 4 – Inbox rule creation
Attackers logged in and created inbox rules to delete incoming emails and mark messages as read, hiding their activity. - Stage 5 – Phishing spread
Using the compromised account, attackers sent over 600 phishing emails to internal and external contacts and distribution lists. - Stage 6 – BEC activity
Attackers monitored replies, removed warning emails, and responded to questions to make the phishing appear legitimate. - Stage 7 – Account compromise expansion
Additional users who clicked the link were compromised through the same AiTM technique, allowing the attack to spread further.

“The recipients of the phishing emails from within the organization who clicked on the malicious URL were also targeted by another AiTM attack. Microsoft Defender Experts identified all compromised users based on the landing IP and the sign-in IP patterns.” states the report published by Microsoft.
Microsoft Defender XDR detects AiTM phishing by spotting suspicious sign-ins across multiple accounts and malicious inbox rules on compromised mailboxes. Defender Experts rapidly contained the attack by disrupting AiTM activity, auto-purging phishing emails, and helping customers recover affected identities. The researchers pointed out that effective remediation went beyond password resets and included revoking session cookies, undoing attacker-made MFA changes, and removing malicious inbox rules. Because AiTM steals active sessions, password resets alone are not enough. Microsoft stresses the continued importance of MFA, combined with conditional access policies, continuous access evaluation, advanced anti-phishing tools, and ongoing monitoring of risky sign-ins to reduce exposure and limit attacker persistence.
Microsoft provided recommendations and mitigations to reduce the impact of this threat.
Have You Seen Her? Endangered Philadelphia Woman Julianna Mishoe Missing from 22nd District
The Philadelphia Police Department is asking for the public's help in locating…
How to Unlock Peak Performance and Overclock Your Samsung Galaxy S22 Today
In the fast-paced ecosystem of mobile computing, squeezing every ounce of performance…
B&H Photo Video Lawsuits: Shocking Settlement Records Revealed
NEW YORK — Retail giant B&H Photo Video has built an international…
Fighter aviation of the Socialist Federal Republic of Yugoslavia in the 1940s and 1950s
Almost immediately after the end of World War II, Josip Broz Tito,…
Congressman Scott Perry Exposes Major Washington Overreach During Live TeleTown Hall
Rep. Scott Perry (R-PA) recently connected with constituents across Pennsylvania's 10th Congressional…
Samsung Odyssey Neo G9 Review: Why This Massive Ultrawide Dominates Gaming
When Samsung first introduced the Odyssey series, it disrupted the ultra-wide display…