

Shadowserver researchers found 6,000+ SmarterMail servers exposed online and likely vulnerable to a critical auth bypass flaw.
Nonprofit security organization Shadowserver reported that over 6,000 SmarterMail servers are exposed on the internet and likely vulnerable to attacks exploiting a critical authentication bypass flaw tracked as CVE-2026-23760. Cybersecurity firm watchTowr disclosed the vulnerability on January 8, and SmarterTools addressed it on January 15, without assigning a CVE.
“SmarterTools SmarterMail versions prior to build 9511 contain an authentication bypass vulnerability in the password reset API. The force-reset-password endpoint permits anonymous requests and fails to verify the existing password or a reset token when resetting system administrator accounts.” reads the advisory. “An unauthenticated attacker can supply a target administrator username and a new password to reset the account, resulting in full administrative compromise of the SmarterMail instance.”
watchTowr researchers released a proof-of-concept exploit that only needs the admin username.
An unauthenticated attacker can exploit the flaw to hijack administrator accounts and achieve remote code execution on the target, potentially leading to a full takeover of vulnerable servers.
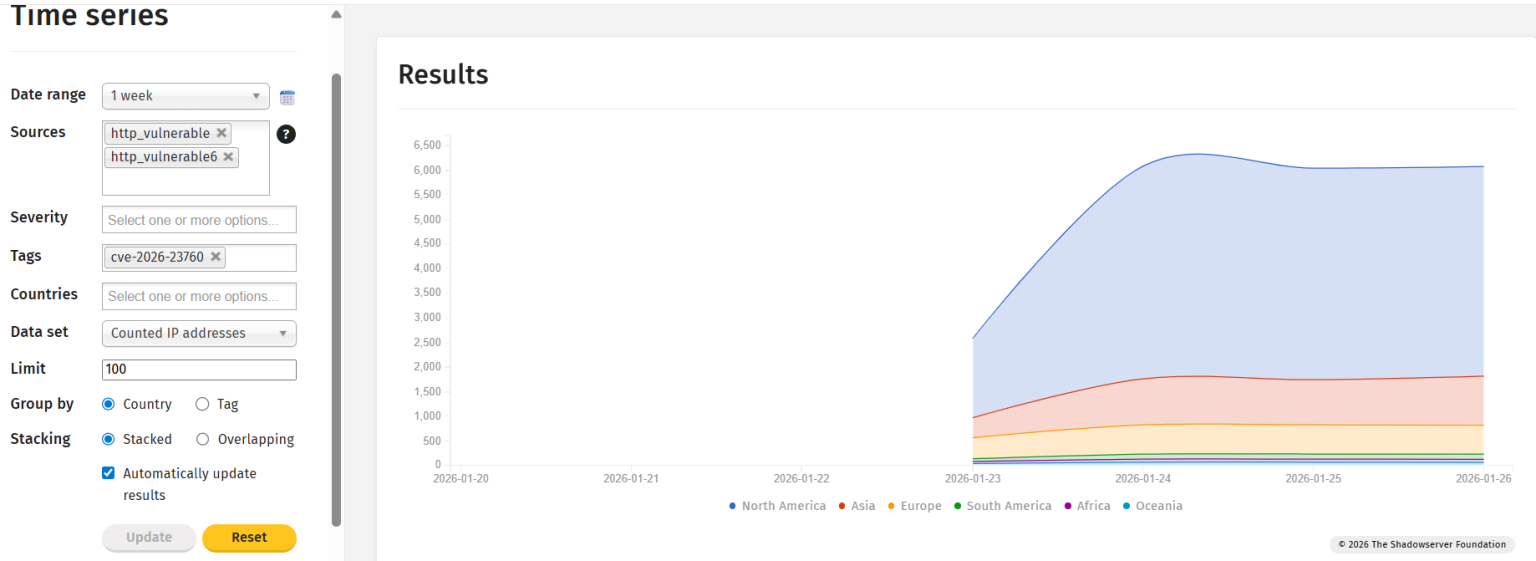
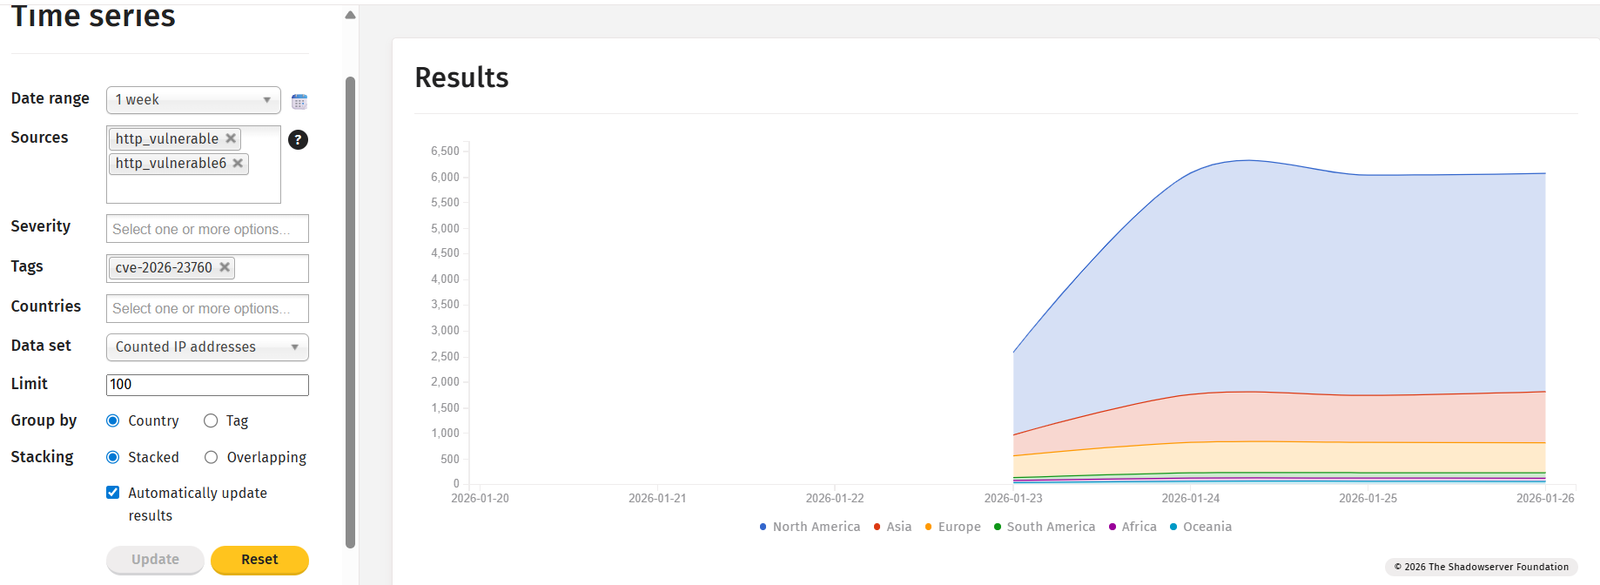
Shadowserver reported that over 6,000 SmarterMail servers are likely vulnerable, based on their version check. The researchers also observed exploitation attempts in attacks in the wild.
Most of the likely vulnerable servers are in the U.S. (4.1K), followed by Malaysia (449), India (188), Canada (166), and the U.K. (146).
KelTec P32 Pocket Pistol Tested: Why Competitors Failed the Ultimate Ballistics Breakdown
The Undisputed King of Micro-Pistols: Why the KelTec P32 Remains Unmatched When…
Congressman Scott Perry Exposes Major Washington Overreach During Live TeleTown Hall
Rep. Scott Perry (R-PA) recently connected with constituents across Pennsylvania's 10th Congressional…
US Air Force considers restarting C-17 Globemaster III production as replacement moves toward 2040s
The United States Air Force Air Mobility Command is examining the feasibility…
Crucial RAM Buying Guide Reveals Massive PC Upgrades Every Builder Needs Right Now
Welcome back to the workbench, Philly tech enthusiasts. Whether you are piecing…
Panic in the US Congress: Not enough planes!
It's been said many times that fighting with numbers is a complete…
Congressman Scott Perry Exposes Crucial House Debates and Major Policy Issues Ahead
In a recent outreach event connecting directly with constituents, U.S. Representative Scott…

This week, CISA added CVE-2026-23760 to its KeV catalog, ordering FCEB agencies to address the identified vulnerability by February 16, 2026.