

Cloudflare fixed a flaw in its ACME validation logic that could let attackers bypass security checks and access protected origin servers.
Cloudflare fixed a flaw in its ACME HTTP-01 validation logic that could let attackers bypass security checks and reach origin servers. The issue stemmed from how Cloudflare’s edge handled requests to the /.well-known/acme-challenge/ path. The company says it found no signs of malicious exploitation.
ACME is a protocol that lets certificate authorities verify domain ownership. With HTTP-01, the CA checks a one-time token at a specific URL. If it matches, the certificate is issued. The process should allow access only to that exact path, and nothing else.
While testing applications behind Cloudflare with a WAF blocking all but specific sources, researchers noticed requests to /.well-known/acme-challenge/{token} bypassed the WAF, reaching the origin server directly.
Demo hosts confirmed the behavior: normal paths returned Cloudflare block pages, but ACME paths returned origin-generated responses (404s) without a real token. A stable, pending HTTP-01 token was created via a custom hostname to reliably test WAF behavior globally.
When Cloudflare’s WAF let /.well-known/acme-challenge/... bypass protections, the trust boundary shifted from WAF to origin. Demo apps showed the risk: Spring/Tomcat endpoints exposed sensitive env variables, Next.js SSR pages leaked operational details, and PHP routing exposed files via LFI bugs. Account-level WAF rules were ignored on this path, enabling header-based attacks (SSRF, SQLi, cache poisoning). Cloudflare fixed the issue on October 27, 2025, restoring consistent WAF enforcement.
“When WAF rules that police headers are skipped, entire classes of issues regain a route to the origin: header driven SQL concatenation in legacy code, SSRF and host confusion via X-Forwarded-Host or X-Original-URL, cache key poisoning when caches vary on headers, method override tricks with X-HTTP-Method-Override, and debug toggles wired to custom headers.” reads the report published by FearsOff. “The obvious question follows – how many apps still trust headers more than they should, and how many rely on the WAF to stand between that trust and the internet?”
Crucial Latino Voter Shift in Lehigh Valley Could Decide the Pennsylvania Election
ALLENTOWN, Pa. — As the race for the White House and control…
Insects Have Six Legs. But This 324-Million-Year-Old Insect Had 24 Legs and a Body Unlike Anything Alive Today
For nearly 40 years, one of the strangest insects ever found was…
BREAKING NEWS: Josh Shapiro’s Administration Rocked by Explosive Harassment Allegations and Deletion of Public Records
HARRISBURG, PA — Pennsylvania Governor Josh Shapiro is facing intense political scrutiny…
Uniqlo closing in on H&M with sights set on Zara’s global crown
Uniqlo owner Fast Retailing’s annual revenue climbed 17% to a record ¥3.96…
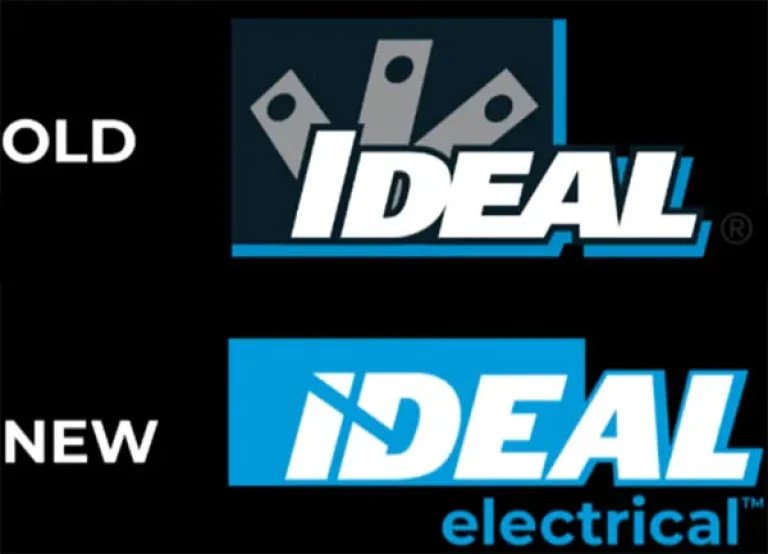
Ideal Electrical has a New Look
Ideal Electrical recently refreshed their logo for the first time in 25…
Not just fighters, not just sixth generation
South Korea has begun developing a concept for a next-generation fighter jet…
WAF bypasses like this grow more dangerous as AI-driven attacks can quickly find and exploit exposed paths. AI can chain small flaws into large attacks, while defenders also use AI to simulate and block threats, making strong WAF protections increasingly vital.
“Vulnerabilities like this WAF bypass take on added urgency with evolving AI-driven attacks. Automated tools powered by machine learning can rapidly enumerate and exploit exposed paths like /.well-known/acme-challenge/, probing for framework-specific weaknesses or misconfigurations at scale.” concludes the report.
Cloudflare addressed the flaw on October 27, 2025.