

A SmarterMail flaw (WT-2026-0001) is under active attack just days after its January 15 patch, with no CVE assigned yet.
A newly disclosed flaw in SmarterTools SmarterMail is being actively exploited just two days after a patch was released. The issue, tracked as WT-2026-0001 and lacking a CVE, was fixed on January 15, 2026, with Build 9511 after responsible disclosure by watchTowr Labs.
SmarterTools SmarterMail is a commercial email server software designed for businesses and service providers. It provides enterprise-level email, calendar, contacts, tasks, and collaboration features.
The flaw is an authentication bypass that lets attackers reset the SmarterMail administrator password via a specially crafted request to the force-reset-password API endpoint.
The vulnerabilities lies in SmarterMail’s APT unauthenticated ForceResetPassword, which trusts an IsSysAdmin flag.
“You may notice that this API endpoint accepts the ForceResetPasswordInputs object, which can be deserialized from the JSON.” reads the report published by Watchtowr.”It has several interesting properties that can be controlled by the user:
IsSysAdminUsernameOldPasswordNewPasswordConfirmPassword
That combination is immediately unusual. Password reset flows typically rely on a second factor or out-of-band proof of control – for example, a secret token delivered via email.”
Massive Star Wars Secret Revealed That Changes Everything You Know Forever
The Star Wars fandom is once again buzzing with speculation as new…
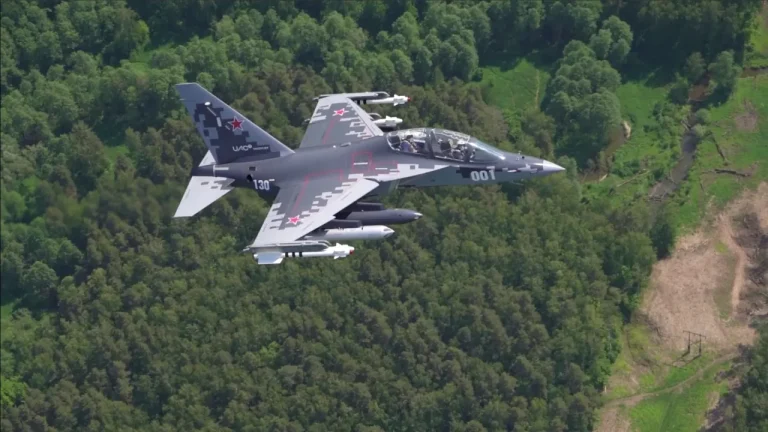
They took it apart piece by piece, so there was a reason
Following a series of reports about what the modernized Yak-130M will look…
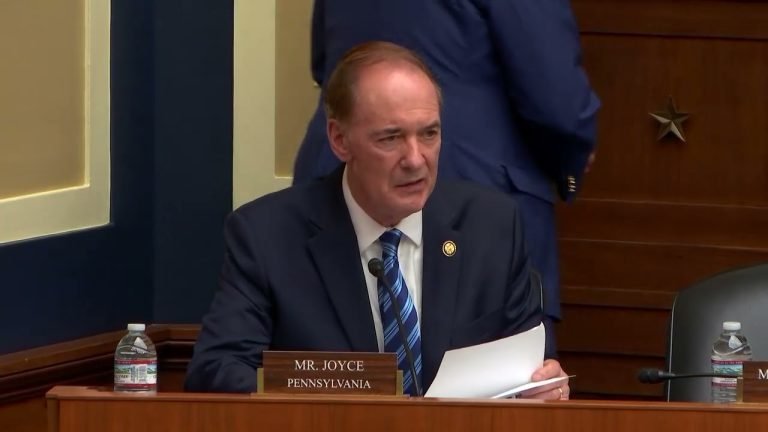
Dr. Joyce Demands Immediate Action on Crucial Data BRIDGE Act in House Markup
WASHINGTON — In a recent high-stakes legislative session, members of the House…
Best RTX 5060 Ti Gaming PC Deal: Save $200 on This 1440p Intel i7 Rig Under $1,500
Score a 1440p-Ready Gaming PC with an RTX 5060 Ti 16GB for…
Fortinet warns of active FortiCloud SSO bypass affecting updated devices
Fortinet confirmed attacks are bypassing FortiCloud SSO authentication, affecting even fully patched…
Former World Chess Champion Kasparov Says US Warned Him About Kremlin Kill Plot
Authored by Chris Summers via The Epoch Times, Former world chess champion…
By setting it to true, an attacker can reset an administrator’s password via a crafted HTTP request, gaining admin access.

This bypass can then be escalated to remote code execution by abusing built‑in admin features to run arbitrary OS commands, leading to SYSTEM‑level access.
“There are no security controls here. No authentication. No authorization. No verification of OldPassword. Despite the API requiring an OldPassword field in the request, it is never checked when resetting a system administrator’s password.” continues the report.
“Ironically, the regular user password reset flow does validate the existing password. The privileged path does not.”
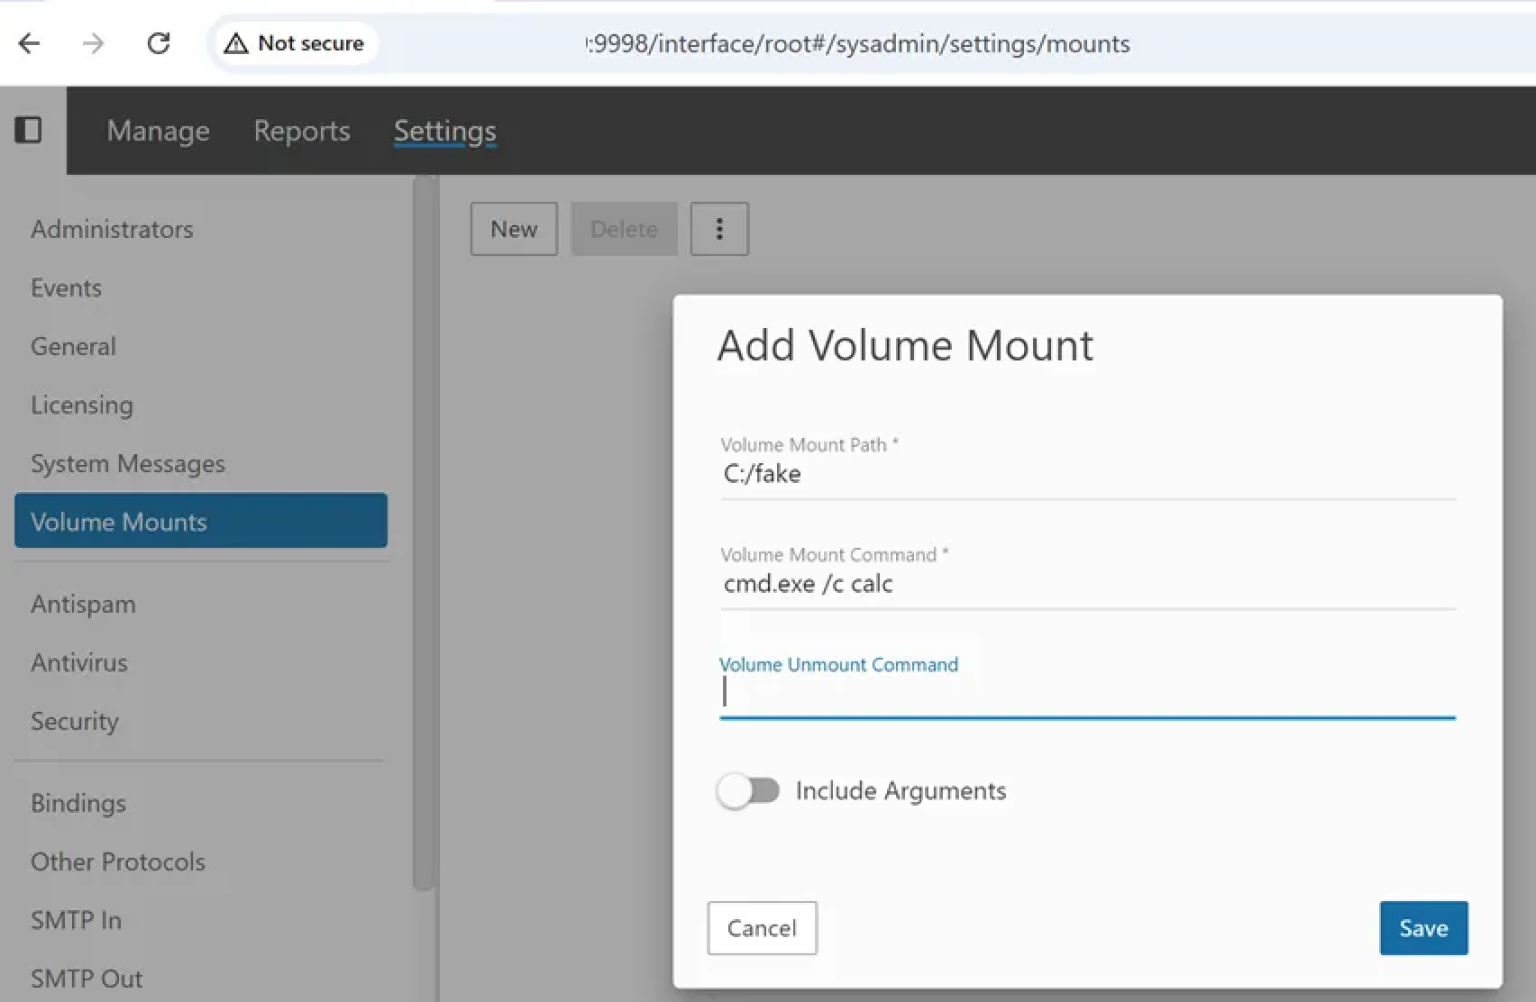
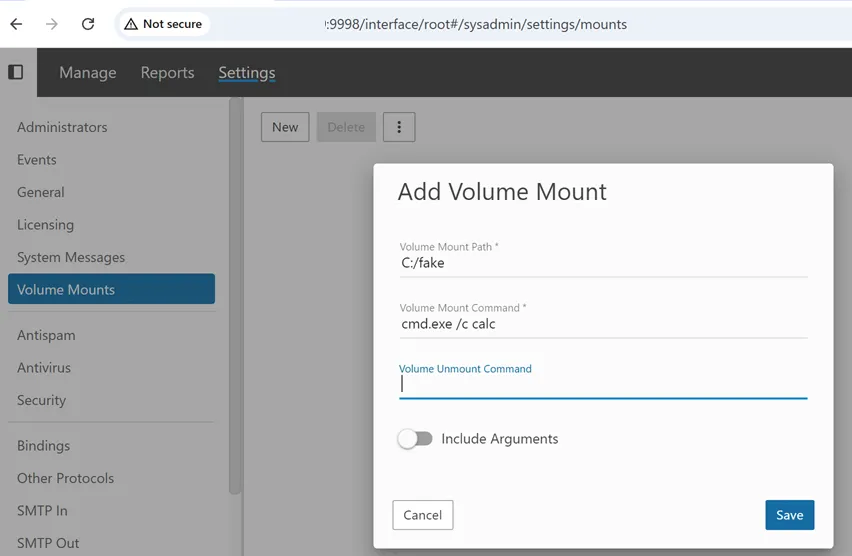
The researchers pointed out that although classified as an authentication bypass, the SmarterMail flaw enables full remote code execution. After gaining system admin access, attackers can use the Volume Mounts feature to run arbitrary OS commands, achieving SYSTEM-level control.

The researchers created a proof of concept that allows achieving a SYSTEM-level shell on the target host.
The issue was patched in version 9511 on January 15, 2026, and is actively exploited. On patched systems, exploit attempts fail due to added password validation checks. No CVE has been assigned yet.
“Once again, this demonstrates that attackers actively monitor release notes and perform patch diffing on high-value targets. Together, friends, we have learned this the hard way today with WT-2026-0001.” concludes the report.
“Given that this vulnerability is already under active exploitation, upgrading is not optional.”