KEEP THE PHILLY PI 100% READER-POWERED

Support Independent Journalism in Philadelphia

HELP THE PHILLY PI DELIVER UNBIASED, COMMUNITY-FOCUSED NEWS

The Philly PI relies on reader support to deliver crucial investigative reporting, breaking news, community safety updates, and transparent tech coverage. Independent journalism requires time, deep research, and absolute editorial freedom—free from paywalls, political influence, or corporate control. We cannot keep our newsroom running without you.

  • 100% READER-FUNDED NEWSROOM

  • NO PAYWALLS OR CORPORATE CONTROL

  • KEEP INDEPENDENT JOURNALISM FREE FOR ALL

LATEST IN SCIENCE & TECH

Simply Sniffing Dark Chocolate Helped Men Squeeze Out 18 More Reps in the Gym During Leg Day

Simply Sniffing Dark Chocolate Helped Men Squeeze Out 18 More Reps in the Gym During Leg Day

Credit: Unsplash. Could the smell of chocolate wafting through the gym make…

Hermit crabs and cockroaches are acting as gardeners for a parasitic plant

Hermit crabs and cockroaches are acting as gardeners for a parasitic plant

Hermit crab. Image via Wiki Commons. In the humid, coastal forests of…

Scientists Found a Real Mummy’s Curse Hiding in the Online Trade in Human Remains

Scientists Found a Real Mummy’s Curse Hiding in the Online Trade in Human Remains

Disturb the dead and disaster may follow. Such is the pharaohs’ curse,…

Shooting Lasers to Read Minds: How LIBS Unlocks the Elemental Secrets of Matter | Philly PI

Shooting Lasers to Read Minds: How LIBS Unlocks the Elemental Secrets of Matter

Imagine firing an invisible beam of light at a mystery rock sitting…

Scientists found 149 new deep-sea species — and a 22-million-year shark-tooth graveyard

Scientists found 149 new deep-sea species — and a 22-million-year shark-tooth graveyard

Closeup detail of an Ophiuroid brittle star collected at Muirfield Seamount, southwest…

The Colorado River Is Drying Up and the West Is Running Out of Easy Choices

The Colorado River Is Drying Up and the West Is Running Out of Easy Choices

Flow in the Colorado River has shrunk by about 20% since 2000,…

$0
Raised
0
Donations
$200
Goal
0%
$

The Philly PI site favicon and logo featuring bold white "PI" lettering on a dark blue background.
LIVE
Subscribe
DONATE
Subscribe
SIGN IN
  • Philly Pulse
  • Politics
  • 2026 Elections
  • Business
  • Security
  • Science & Tech
  • Sports
  • Entertainment
  • Lifestyle
  • People
  • Shopping

Archives

  • November 2026
  • October 2026
  • September 2026
  • August 2026
  • July 2026
  • June 2026
  • May 2026
  • April 2026
  • March 2026
  • February 2026
  • January 2026
  • December 2025
  • December 2024

Categories

  • 2026 Elections
  • Affiliate Resources
  • AI
  • Ammo & Ballistics
  • Business
  • China
  • Comedy
  • Crime
  • Culture
  • Europe
  • Fact Check
  • Firearm Reviews
  • Game Guides
  • Gaming
  • Gaming PCs
  • Gear & Ballistics
  • Hacking
  • Health
  • History
  • IPO Watch
  • Iran
  • Israel
  • Japan
  • Lifestyle
  • Market Recon
  • Mexico
  • Military & Defense
  • Military History
  • Missing Person
  • Movies
  • News
  • Opinion
  • People
  • Politics
  • Range & Shooting Sports
  • Russia
  • Saudi Arabia
  • Science
  • Security
  • Shopping
  • Somalia
  • Sport
  • Startups
  • Tech
  • Travel
  • Ukraine
  • Uncategorized
  • Venezuela
  • Video
  • World
★
Midterm Elections 2026
Balance of Power
54 Majority Won Senate (51 to win) 44
● Democrats Republicans ●
253 Majority Won House (218 to win) 150
Saturday, Nov 14, 2026
LIVE
Subscribe
Donate
Philly PI
Donate
bitcoin
Bitcoin (BTC) $ 64,624.00 5.89%
ethereum
Ethereum (ETH) $ 1,782.13 8.12%
solana
Solana (SOL) $ 70.61 11.32%
bnb
BNB (BNB) $ 582.76 8.30%
dogecoin
Dogecoin (DOGE) $ 0.057808 11.08%
cardano
Cardano (ADA) $ 0.14867 12.25%
tron
TRON (TRX) $ 0.307683 1.57%
monero
Monero (XMR) $ 475.78 10.77%
litecoin
Litecoin (LTC) $ 44.50 10.18%
kucoin-shares
KuCoin (KCS) $ 6.17 5.41%
binance-bridged-usdc-bnb-smart-chain
Binance Bridged USDC (BNB Smart Chain) (USDC) $ 0.999945 0.02%
jupiter-exchange-solana
Jupiter (JUP) $ 0.242893 7.53%
Philly PI
  • Philly Pulse
  • Politics & World
  • Business
  • Sports
  • Entertainment
Search
  • Philly Pulse
  • Politics & World
  • Business
  • Tech & Science
  • Sports
  • Gaming
  • Shopping
Have an existing account? Sign In
Follow US
© 2026 The Philadelphia Post-Intelligencer.
Ideal Electrical Tools Logo Old vs New 2026 Branding Change

Ideal Electrical has a New Look

A U.S. Air Force C-40 executive transport aircraft, based on the Boeing 737-700. The U.S. Air Force plans to acquire a Boeing 737 MAX under a $250 million C-40 fleet expansion, marking the first military use of the newer 737 MAX generation.

U.S. Air Force to Buy First Boeing 737 MAX for Military Transport Service With $250M Funding

As French Riots Escalate, 'Wild Horde' Beats Police Commander Unconscious, Stomps His Head

As French Riots Escalate, 'Wild Horde' Beats Police Commander Unconscious, Stomps His Head

Rep. Dan Meuser at House Small Business Committee Hearing

Rep. Dan Meuser at House Small Business Committee Hearing

Wanted: Suspect for Burglary in the 9th District [VIDEO]

PHILADELPHIA POLICE WATCH: Video Released of Suspect in 9th District Burglary

Dr. Joyce Exposes William Swartzwelder’s Crucial 70-Year Legacy of Public Service

Dr. Joyce Exposes William Swartzwelder’s Crucial 70-Year Legacy of Public Service

Klein Marker Leash on Construction Worker

Klein Makes a Leash for Your Construction Markers

Strategic Assessment: US Reportedly Limits Starlink Terminal Speeds for Ukrainian Forces in Motion

Strategic Assessment: US Reportedly Limits Starlink Terminal Speeds for Ukrainian Forces in Motion

Massive Star Wars Secret Revealed: What Every Streamer Needs To Know Right Now

Massive Star Wars Secret Revealed: What Every Streamer Needs To Know Right Now

Hacking

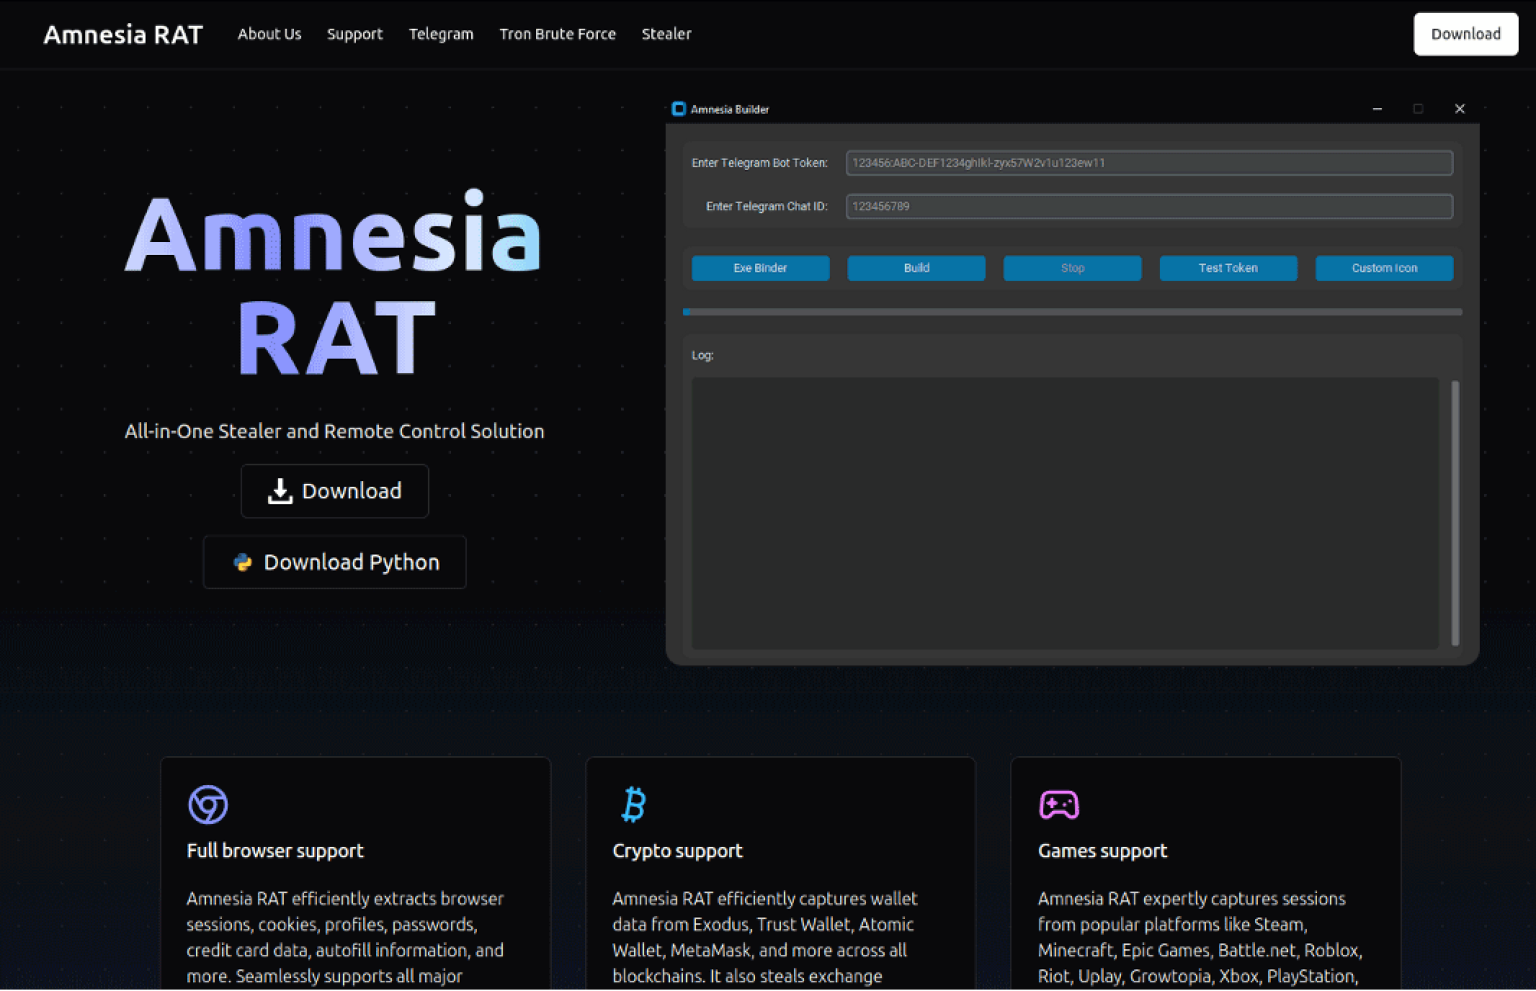
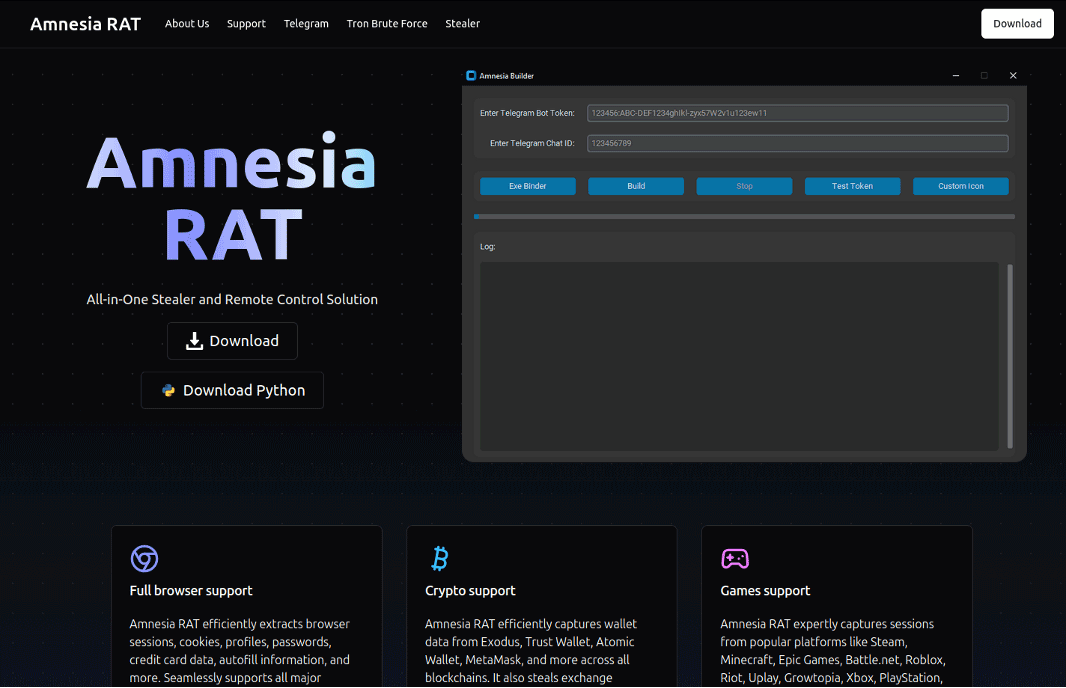
Amnesia RAT deployed in multi-stage phishing attacks against Zelensky users

Amnesia RAT deployed in multi-stage phishing attacks against Zelensky users

A multi-stage phishing campaign targets users in Russia with ransomware and Amnesia RAT using fake business documents as lures.

FortiGuard Labs researchers uncovered a multi-stage malware campaign mainly targeting users in Russia. The attack uses fake business documents as social engineering lures to distract victims while malware runs in the background. It escalates to full system compromise, deploying Amnesia RAT and ransomware, disabling Microsoft Defender via the Defendnot tool, and abusing GitHub and Dropbox to host payloads and evade detection.
Amnesia RAT deployed in multi-stage phishing attacks against Zelensky users

“The threat actors further increase resilience by separating payload hosting across multiple public cloud services. GitHub is primarily used to distribute scripts, while Dropbox hosts binary payloads.” reads the report published by FortiGuard Labs. “This modular hosting approach allows attackers to update or rotate components independently, complicates takedown efforts, and helps malicious traffic blend into legitimate enterprise network activity.”

Amnesia RAT deployed in multi-stage phishing attacks against Zelensky users | Philly PI

The attack chain starts when a victim opens a compressed archive that looks like normal business material. The archive contains fake accounting files with Zelensky names that match everyday work tasks. Inside, a shortcut file pretends to be a text document for accountants. When the user clicks it, the file launches PowerShell and downloads a script from GitHub. The threat actors do not use exploits; they rely entirely on user interaction, which makes it effective in corporate environments.

The PowerShell script, called kira.ps1, acts as a loader. It hides the PowerShell window to avoid suspicion and creates a fake accounting document on the system. The script opens this document to keep the user busy while malware runs in the background. It also sends a message to the attacker via Telegram to confirm the infection. After a short delay, it downloads and runs an obfuscated VBScript in hidden mode.


What do you think? Post a comment.


“Once written to disk, the decoy document is automatically opened. This reinforces the appearance of a legitimate business task and keeps the user engaged while malicious activity continues in the background.” continues the report. “After establishing this distraction, the script sends an execution confirmation to the attacker using the Telegram Bot API. The message includes user-context information, allowing the attacker to verify that the initial stage has been executed successfully on a live system.”

This second script works as the main controller. It stays encoded on disk and rebuilds the real malicious code only in memory using Base64 and RC4 decoding. This approach limits detection. The final stage initializes system objects, checks for administrator rights, and repeatedly triggers UAC prompts until it gains elevated privileges. Once ready, the malware moves to its final operational phase and continues the attack.
- Advertisement -

EXPLORE MORE

Rep. Perry Unveils Major SURFACE Act Legislation in Crucial House Address

Rep. Perry Unveils Major SURFACE Act Legislation in Crucial House Address

As Capitol Hill navigates a packed legislative calendar, lawmakers continue to introduce…
The internet isn’t the best place to find upgrades for your computer — brick-and-mortar stores still reign supreme thanks to bundled deals


By

Stewart Bendle 

Published 15 October 26


Premium
Component bundles are a great way of offsetting high prices on certain parts, but your proximity to a Micro Center may save you even more.

Why Micro Center Bundles Make Local PC Hardware Stores King for High-Value Upgrades

The Consumer PC Hardware Crisis: Why Brick-and-Mortar Stores Reign Supreme The rising…
Wanted: Suspect for Vandalism in the 5th District [VIDEO]

Philadelphia Police Need Help Identifying Suspect in 5th District Vandalism Case [Watch Video]

PHILADELPHIA — Police in Northwest Philadelphia are asking for the public's help…

Rep. Meuser on Fox News

Rep. Meuser on Fox News

As legislative battles intensify on Capitol Hill, key members of the U.S.…

Shocking FaceTime Scam Exposes Georgia Man Arrested for Indecent Exposure

Shocking FaceTime Scam Exposes Georgia Man Arrested for Indecent Exposure

PHILADELPHIA — Local authorities across the Greater Philadelphia region are urging residents…

Russia Unveils Strategic PD-8V Turboshaft Engine Development Project for Heavy Helicopters

Geopolitical & Defense Intelligence Update: Russian Aerospace Propulsion Development The Russian defense-industrial…

In the final phase, the malware launches its most damaging actions after disabling defenses and blocking recovery. It installs Amnesia RAT to maintain long-term control and steal data. The RAT hides as “svchost.scr”, gains persistence, and steals browser credentials, Telegram sessions, crypto wallets, Discord and Steam data, seed phrases, and detailed system information. It also enables screenshots, audio capture, remote commands, and data exfiltration through Telegram and file-hosting services.

“Amnesia RAT is designed for broad, multi-category data theft combined with real-time surveillance and system control.” continues the report.

Amnesia RAT deployed in multi-stage phishing attacks against Zelensky users | Philly PI

Afterward, the attack deploys Hakuna Matata ransomware. This payload encrypts a wide range of files, adds a custom extension, drops ransom notes, changes the wallpaper, kills key processes, and replaces crypto addresses in the clipboard. In parallel, a WinLocker component fully blocks the desktop and shows messages that pressure victims to contact attackers quickly.

“The ransomware maintains a continuous execution loop that actively monitors and hijacks clipboard contents, replacing cryptocurrency wallet addresses with attacker-controlled values.” continues the report. “Combined with encryption, lockout mechanisms, and coercive visual messaging, these behaviors demonstrate an attack model built for maximum leverage, sustained control, and financial extraction.”

Together, these steps ensure maximum disruption, control, and financial leverage.

“This attack chain demonstrates how modern malware campaigns can achieve full system compromise without exploiting software vulnerabilities.” concludes the report. “Instead, the threat actor relies on social engineering, widely trusted platforms such as GitHub and Dropbox, and the abuse of legitimate operating system functionality to stage, deliver, and execute payloads while blending into normal enterprise traffic.”

Pierluigi Paganini


Share This Article
Facebook Telegram Threads Copy Link Print
By
Tommy Graham
October 24, 2026
Share
Picture of Tommy Graham

Tommy Graham

All Posts

JOIN THE CONVERSATION

Subscribe
Connect with
Login
I allow to create an account
When you login first time using a Social Login button, we collect your account public profile information shared by Social Login provider, based on your privacy settings. We also get your email address to automatically create an account for you in our website. Once your account is created, you'll be logged-in to this account.
DisagreeAgree
Notify of
guest
Connect with
I allow to create an account
When you login first time using a Social Login button, we collect your account public profile information shared by Social Login provider, based on your privacy settings. We also get your email address to automatically create an account for you in our website. Once your account is created, you'll be logged-in to this account.
DisagreeAgree
guest
0 Comments
Oldest
Newest Most Voted

Top stories

Dr. Joyce Slams Critics and Unveils Major Pennsylvania Voter Hall of Fame Tribute

Dr. Joyce Slams Critics and Unveils Major Pennsylvania Voter Hall of Fame Tribute

WASHINGTON — In a special congressional tribute highlighting civic…

Launch Offer: Save on the New BLUETTI Elite 300 Portable Power Station
Iran "Decision Week": Trump Teases "Easy Way Or Hard Way" As Tankers Burn, Rial Craters And Tehran's Oil Minister Quits

Iran "Decision Week": Trump Teases "Easy Way Or Hard Way" As Tankers Burn, Rial Craters And Tehran's Oil Minister Quits

Seven months into the war, the Iran story has…

zerohedge logo

America's Wile E. Coyote Moment

Authored by Matthew Piepenburg via VonGreyerz.gold, When it comes…

Dr. Joyce Slams Retiring Official in Major House Floor Tribute and Farewell Address

Dr. Joyce Slams Retiring Official in Major House Floor Tribute and Farewell Address

As life on Capitol Hill frequently revolves around high-stakes…

Massive Director's Commentary Uncovers Shocking Secrets Behind The Iconic Vader Episode II Scene

Massive Director’s Commentary Uncovers Shocking Secrets Behind The Iconic Vader Episode II Scene

The vast, ever-expanding galaxy far, far away continues to…

50 Iranian Tanker Logjam Unfolds As US Naval Blockade Starves Tehran Of Oil Revenue

50 Iranian Tanker Logjam Unfolds As US Naval Blockade Starves Tehran Of Oil Revenue

Bloomberg cites a new report from United Against Nuclear…

Massive Late Summer Breakdown Reveals The 5 Best Prebuilt Gaming PCs Dominating 2026

Massive Late Summer Breakdown Reveals The 5 Best Prebuilt Gaming PCs Dominating 2026

As we navigate through the hardware cycles of late…

Strategic Strikes Hit Vessels in Bug Estuary and Chornomorsk Port Region

Strategic Strikes Hit Vessels in Bug Estuary and Chornomorsk Port Region

Advanced loitering munition tactical deployment over maritime target area…

Turkish Cargo Ship Sunk By Drone Strike Off Romania, Two Sailors Killed

Turkish Cargo Ship Sunk By Drone Strike Off Romania, Two Sailors Killed

There's no doubt that the tit-for-tat war on Black…

Meuser on National Report

Meuser on National Report

As Capitol Hill navigates a dense legislative calendar and…

Related Articles

Ransomware attack on Ingram Micro impacts 42,000 individuals
Hacking

Ransomware attack on Ingram Micro impacts 42,000 individuals

By
Tommy Graham
3 Min Read
Critical TP-Link VIGI camera flaw allowed remote takeover of surveillance systems
Hacking

Critical TP-Link VIGI camera flaw allowed remote takeover of surveillance systems

By
Tommy Graham
2 Min Read
ACME flaw in Cloudflare allowed attackers to reach origin servers
Hacking

ACME flaw in Cloudflare allowed attackers to reach origin servers

By
Tommy Graham
3 Min Read
Cisco fixed actively exploited Unified Communications zero day
Hacking

Cisco fixed actively exploited Unified Communications zero day

By
Tommy Graham
3 Min Read
Arctic Wolf detects surge in automated Fortinet FortiGate firewall configuration attacks
Hacking

Arctic Wolf detects surge in automated Fortinet FortiGate firewall configuration attacks

By
Tommy Graham
2 Min Read
U.S. CISA adds Prettier eslint-config-prettier, Vite Vitejs, Versa Concerto SD-WAN orchestration platform, and Synacor Zimbra Collaboration Suite flaws to its Known Exploited Vulnerabilities catalog
Hacking

U.S. CISA adds Prettier eslint-config-prettier, Vite Vitejs, Versa Concerto SD-WAN orchestration platform, and Synacor Zimbra Collaboration Suite flaws to its Known Exploited Vulnerabilities catalog

By
Tommy Graham
3 Min Read

Free Philly PI Newsletter

Brings you a selection of the latest news, trends, insights, and tips from around the world.

You’ve been successfully subscribed to our newsletter!

Philly PI

Sections & Features

  • Philly Pulse
  • Politics & World
  • Business
  • Tech & Science
  • Sports
  • Gaming
  • Shopping


  • Entertainment
  • Tech
  • Health
  • Fact Check
  • Crime Report

In-Focus

  • Iran War
  • Indie Vanguard Awards Hub
  • On air
  • Write for The Philly PI
  • Sign up / Login
  • Donate
  • Advertise
  • Privacy Policy
  • Terms Of Use
  • Subscription Terms
  • Sitemap
  • Philly Pulse
  • Politics & World
  • Business
  • Sports
  • Entertainment

© 2026 The Philadelphia Post-Intelligencer. All Rights Reserved. The Philadelphia Post-Intelligencer is your trusted source for comprehensive and balanced news coverage. With a commitment to integrity and accuracy, we provide in-depth reporting that uncovers the stories that matter most.

The Philly PI Newsletter
  • Daily Stories
  • Stock Arlets
  • Full Acess
Subscribe to our newsletter to get our newest articles instantly!

You’ve been successfully subscribed to our newsletter!

$0
Raised
0
Donations
$200
Goal
0%
$

The Philly PI Newsletter
  • Daily Stories
  • Stock Arlets
  • Full Acess
Subscribe to our newsletter to get our newest articles instantly!

You’ve been successfully subscribed to our newsletter!

$0
Raised
0
Donations
$200
Goal
0%
$

wpDiscuz
Welcome Back!

Sign in to your account

Username or Email Address
Password

Lost your password?

Not a member? Sign Up