

Microsoft issued emergency updates to fix an actively exploited Office zero-day, CVE-2026-21509, affecting Office 2016–2024 and Microsoft 365 Apps.
Microsoft released out-of-band security updates to address an actively exploited Office zero-day vulnerability tracked as CVE-2026-21509.
The issue is a security feature bypass vulnerability that affects multiple Office versions, including Microsoft Office 2016, Microsoft Office 2019, Microsoft Office LTSC 2021, Microsoft Office LTSC 2024, and Microsoft 365 Apps for Enterprise.
“Reliance on untrusted inputs in a security decision in Microsoft Office allows an unauthorized attacker to bypass a security feature locally.” reads the advisory that confirms that the issue is actively exploited in the wild. “An attacker must send a user a malicious Office file and convince them to open it.”
The update addresses a flaw that bypasses OLE security protections in Microsoft 365 and Office, exposing users to vulnerable COM/OLE controls.
Microsoft confirmed that the Office Preview Pane is not affected and cannot be used as an attack vector. However the tech giant did not disclose technical details about the attacks exploiting this vulnerability.
Microsoft is working to address the vulnerability in Microsoft Office 2016 and 2019 and announced that security updates will be released as soon as possible.
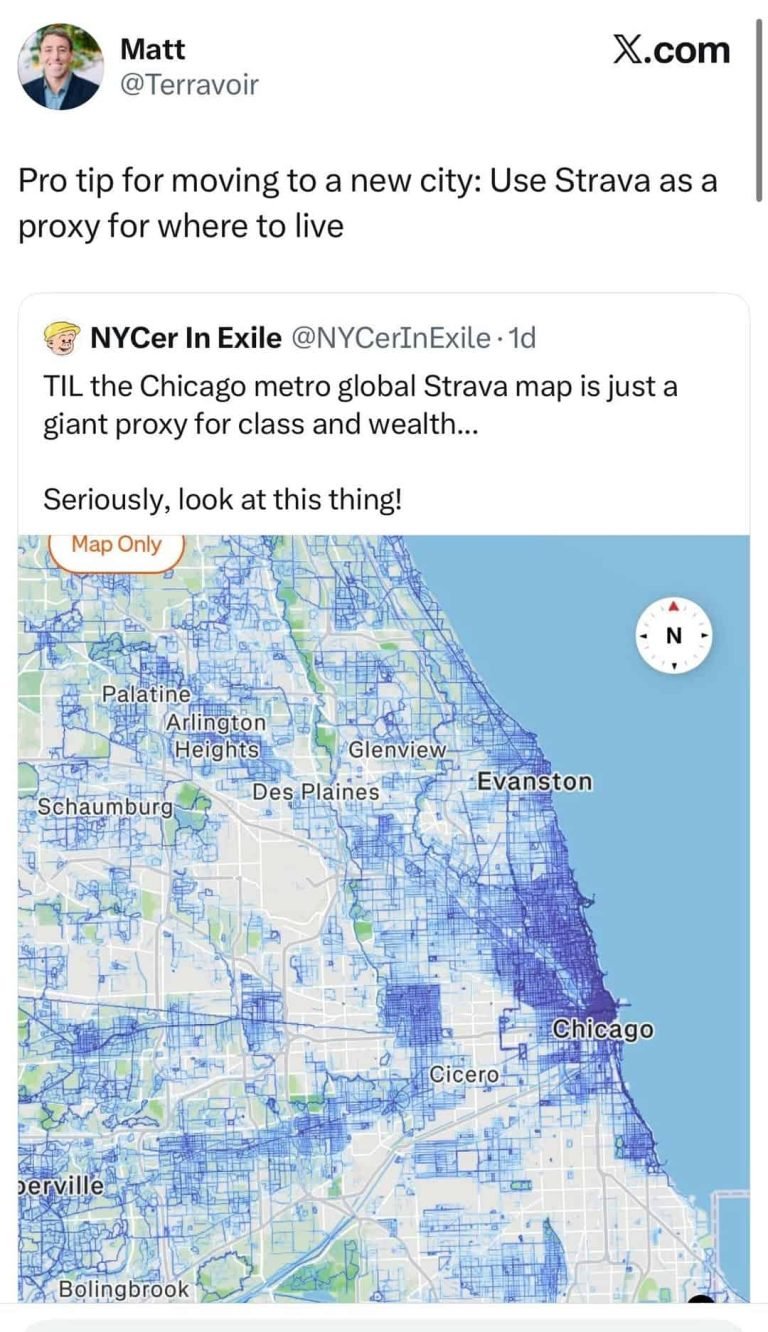
Strava’s Heatmap Is Accidentally Becoming a Map of Where People Want to Live
A map built to help runners find their next route is starting…
Battle of Trafalgar: Strategic Necessity or Aggressive Overreach?
CAPE TRAFALGAR — On October 21, 1805, 27 British warships engaged a…
The Ultimate Gears of War E-Day PvP Guide: Best Modes, Maps, and Strategy Tips
Hey, Gears players! Welcome to our comprehensive Gears of War: E-Day Versus…
Iran Seeking To Increase Range Of Missiles: 'Keep Enemy At Greater Distance'
Just days ago President Trump told a Republican audience at a rally that…
Revealed: How to Score Massive Newegg Promo Codes and Hardware Discounts in 2026
Welcome back to the hardware desk here at The Philly PI, where…
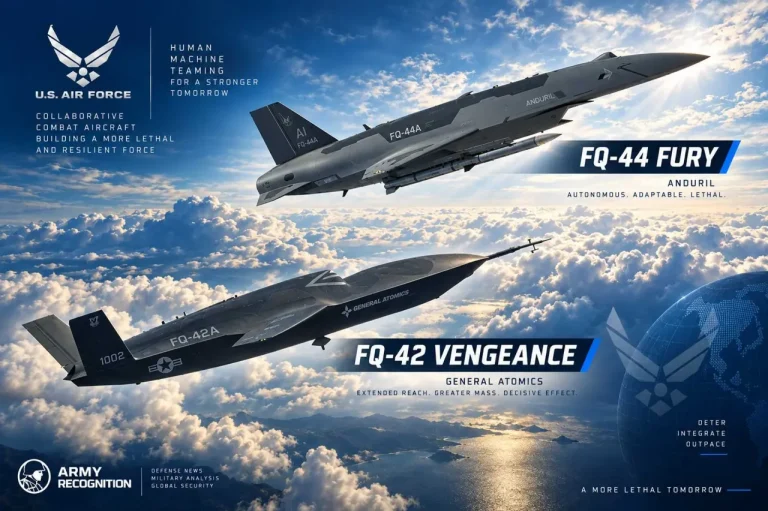
USAF Approves FQ-42 & FQ-44 Collaborative Combat Aircraft
The U.S. Air Force has officially approved the General Atomics FQ-42 Vengeance…
Microsoft provides mitigations to reduce exploitation risk. Office 2021 and later are protected automatically through a service-side fix after restarting apps. Office 2016 and 2019 require installing the upcoming security update or manually applying a registry change to block vulnerable COM/OLE controls. This involves adding a specific COM Compatibility registry key and setting a Compatibility Flags DWORD value. Users should back up the registry before making changes and restart Office for protections to take effect.