

Researchers found over 20 flaws in Dormakaba access systems that could let attackers remotely unlock doors at major organizations.
Researchers from SEC Consult discovered and fixed more than 20 security flaws in Dormakaba physical access control systems.
The experts uncovered multiple critical vulnerabilities in Dormakaba physical access control systems based on exos 9300. These enterprise systems are widely used by large European organizations, including energy firms, logistics companies, and airports, to manage access with key cards or fingerprint readers. Dormakaba said several thousand customers were affected, including some operating in high-security environments.
“These flaws let an attacker open arbitrary doors in numerous ways, reconfigure connected controllers and peripherals without prior authentication, and much more.” reads the report published by the researchers.
Researchers identified multiple flaws in a Dormakaba access control product, including hardcoded credentials, weak passwords, missing authentication, and command injection.
The researchers examined Dormakaba’s exos 9300 physical access control ecosystem, including central management software, access managers, and door-side registration units. Exos 9300 runs on Windows Server, uses an MSSQL database, and manages access devices through networked controllers. The access managers (9200 series) run either Windows CE or Linux and expose multiple services, including web interfaces and a SOAP API used to control locks. They store sensitive data locally, such as credentials, PINs, and configurations.
SEC Consult found flaws that could let attackers unlock doors, steal access PINs, or launch further attacks. Dormakaba pointed out that exploitation would require prior access to the customer’s internal network or hardware. Dormakaba confirmed that a few thousand customers were potentially affected, including some high-security environments. Over 20 vulnerabilities were reported, and the vendor has spent the past 18 months releasing patches, hardening guidance, and working with major customers.
Hackers exploit unsecured MongoDB instances to wipe data and demand ransom
Over 1,400 exposed MongoDB servers have been hijacked and wiped by hackers,…
Ultimate Belorta Pumpkin Witch Build Guide: Best Teams, Skills, and Strategy
Dominate the Battlefield with the Ultimate Goddess of Victory: Nikke Belorta: Pumpkin…
Crucial Latino Voter Shift in Lehigh Valley Could Decide the Pennsylvania Election
ALLENTOWN, Pa. — As the race for the White House and control…
Dragon’s Dogma 2 Dark Arisen: The Ultimate Guide to DLC Changes, Prices, and Beginner Tips
Buying a game or expansion right before it unlocks can be an…
Exposes Five Hidden Newegg Shopping Hacks To Stop Overpaying For PC Parts
Welcome back to the hardware desk here at The Philly PI. If…
Revealed: How to Score Massive Newegg Promo Codes and Hardware Discounts in 2026
Welcome back to the hardware desk here at The Philly PI, where…
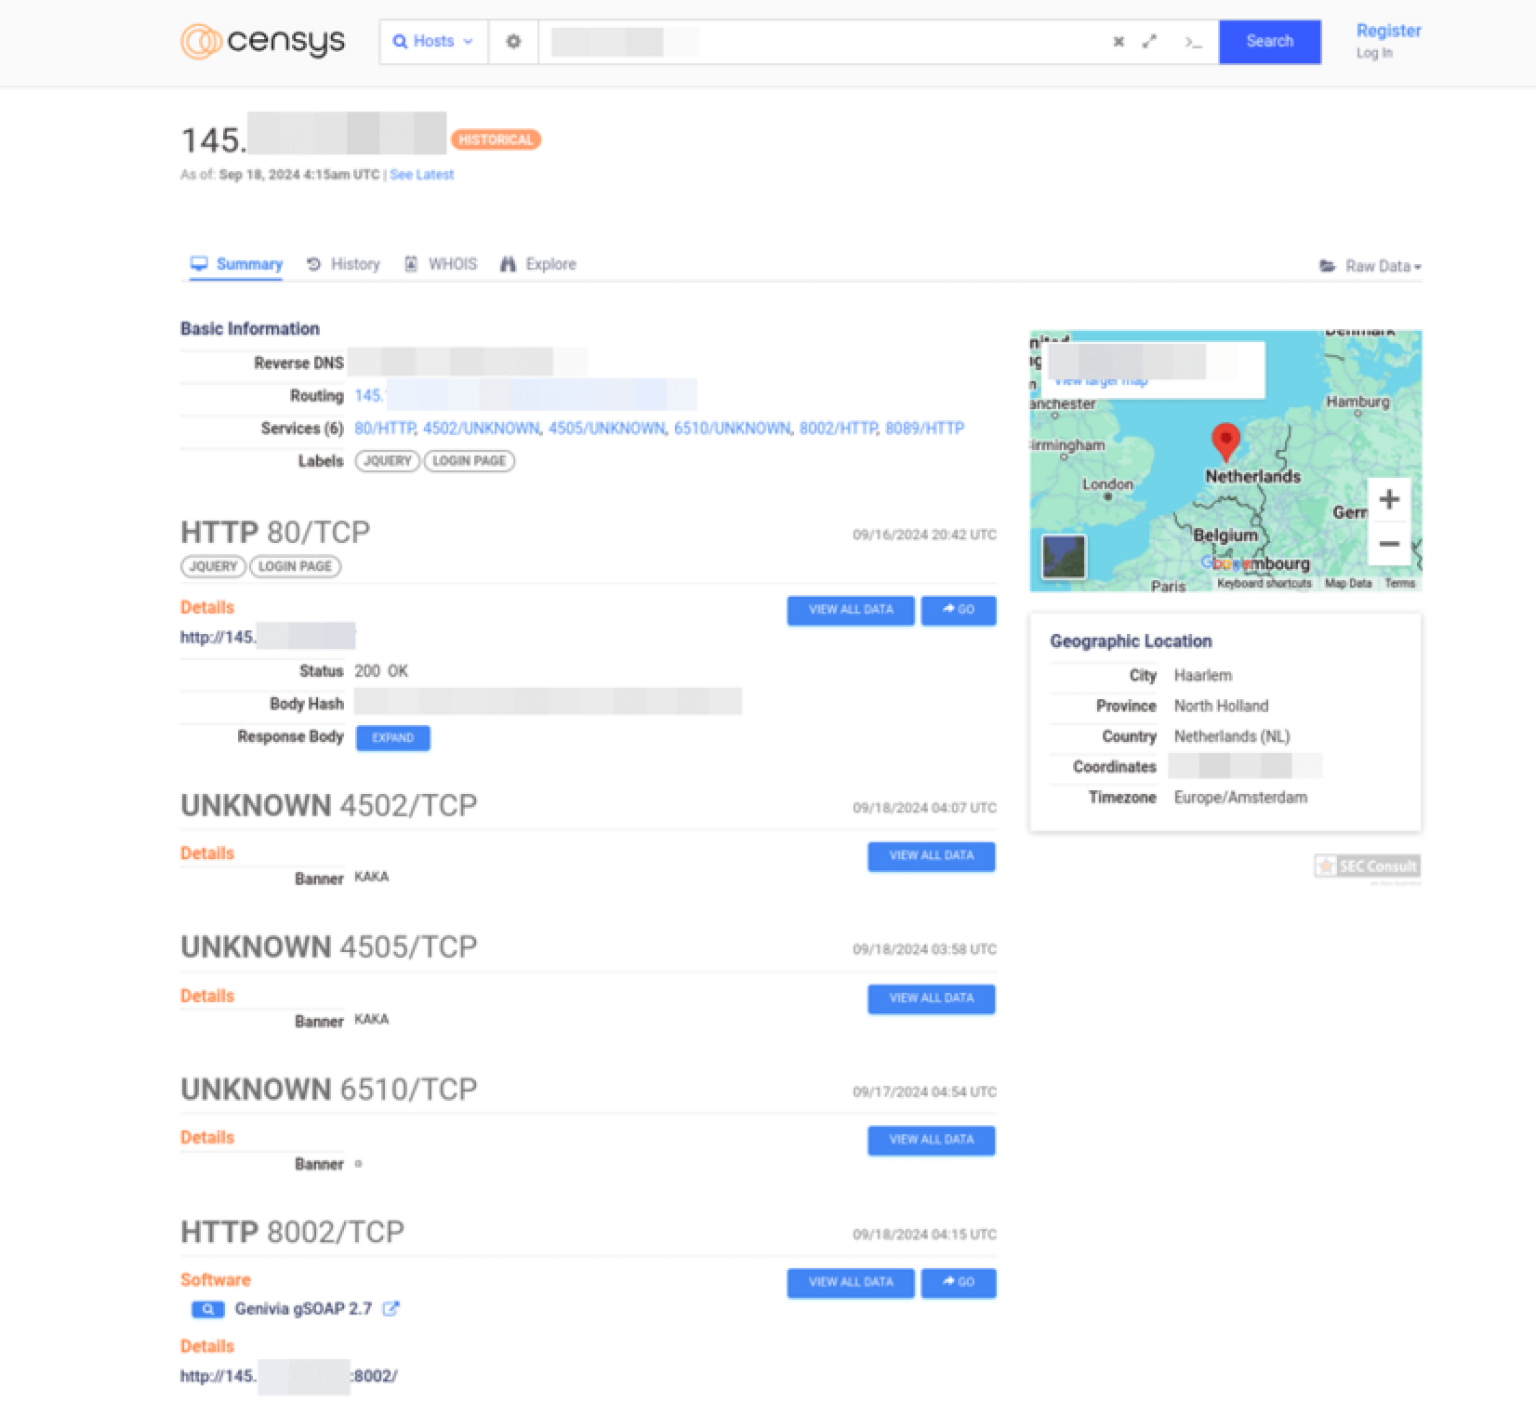
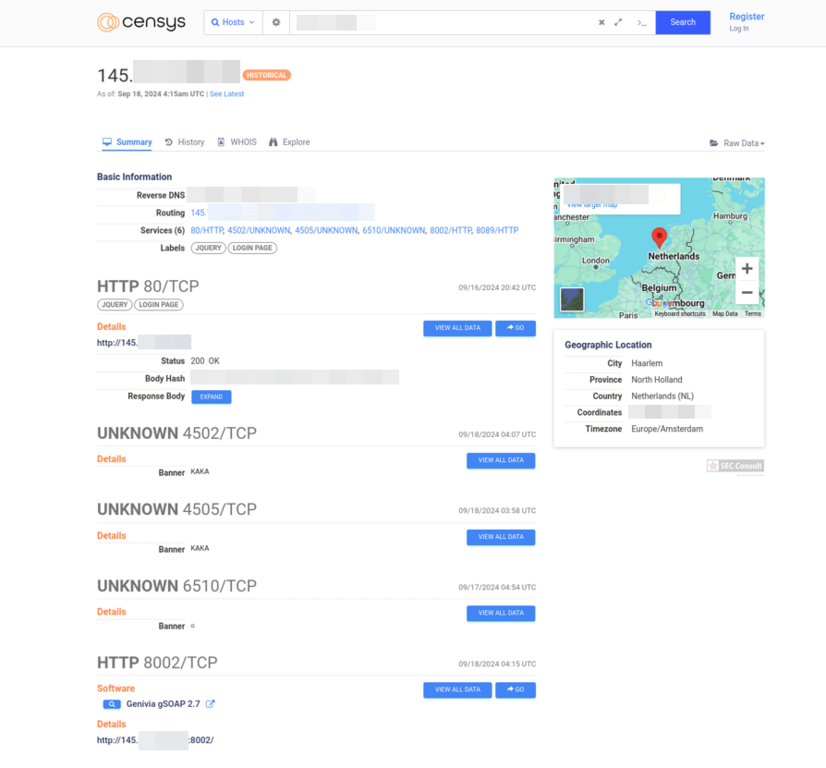
Researchers found some access managers directly exposed to the internet, mainly clustered in countries such as Spain, the Netherlands, and Switzerland. Many had web login pages and the SOAP API on port 8002 publicly accessible, allowing direct control of door relays. If exploited, the identified vulnerabilities could let attackers remotely open doors over the internet.
“Using those fingerprints, we were able to identify some access managers directly available via the internet. It was quite suspicious that they popped up in clusters and mostly in specific countries like Spain and the Netherlands, sometimes Switzerland. Most of the identified access managers on the internet had their web service including the login exposed as well as the SOAP service (Port 8002) to directly control the connected relays and doors.” reads the report. “It would be possible to exploit the vulnerabilities detailed in this blogpost to open doors via the internet.”

The researchers published a PoC video of an attack that opens doors using specially crafted requests.
At the time of this writing, Dormakaba is not aware of any attacks exploiting one of these vulnerabilities in the wild.