

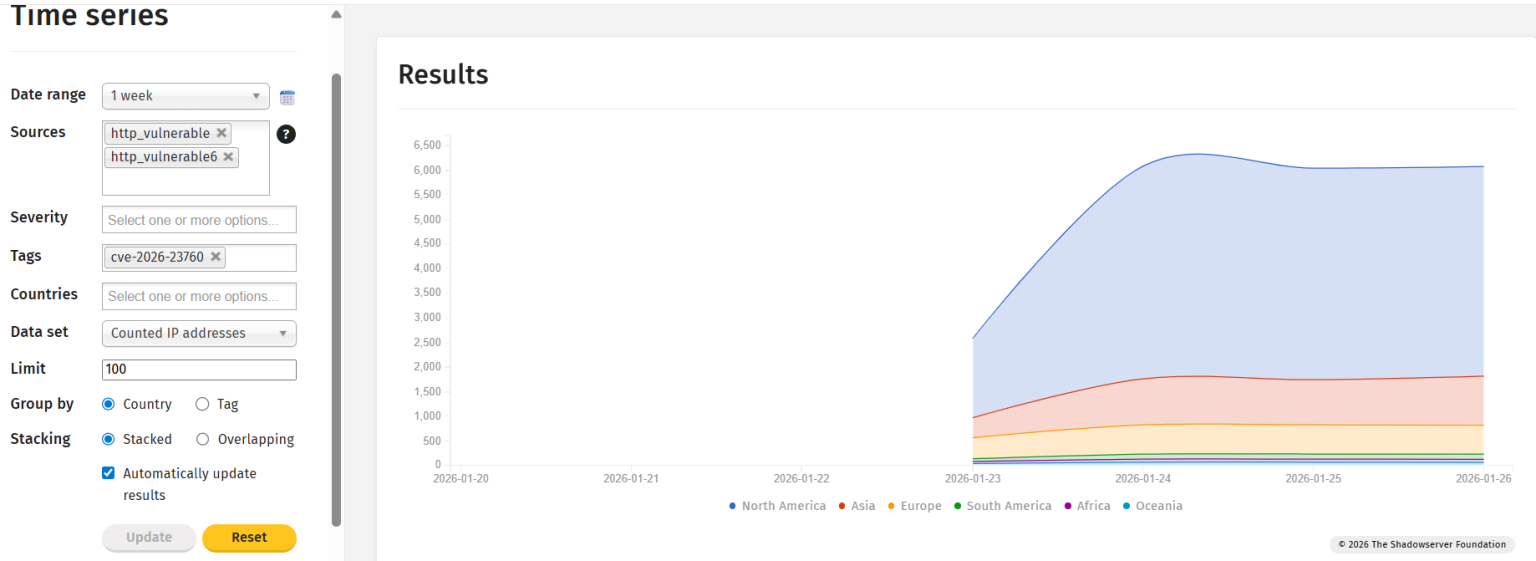
Shadowserver researchers found 6,000+ SmarterMail servers exposed online and likely vulnerable to a critical auth bypass flaw.
Nonprofit security organization Shadowserver reported that over 6,000 SmarterMail servers are exposed on the internet and likely vulnerable to attacks exploiting a critical authentication bypass flaw tracked as CVE-2026-23760. Cybersecurity firm watchTowr disclosed the vulnerability on January 8, and SmarterTools addressed it on January 15, without assigning a CVE.
“SmarterTools SmarterMail versions prior to build 9511 contain an authentication bypass vulnerability in the password reset API. The force-reset-password endpoint permits anonymous requests and fails to verify the existing password or a reset token when resetting system administrator accounts.” reads the advisory. “An unauthenticated attacker can supply a target administrator username and a new password to reset the account, resulting in full administrative compromise of the SmarterMail instance.”
watchTowr researchers released a proof-of-concept exploit that only needs the admin username.
An unauthenticated attacker can exploit the flaw to hijack administrator accounts and achieve remote code execution on the target, potentially leading to a full takeover of vulnerable servers.
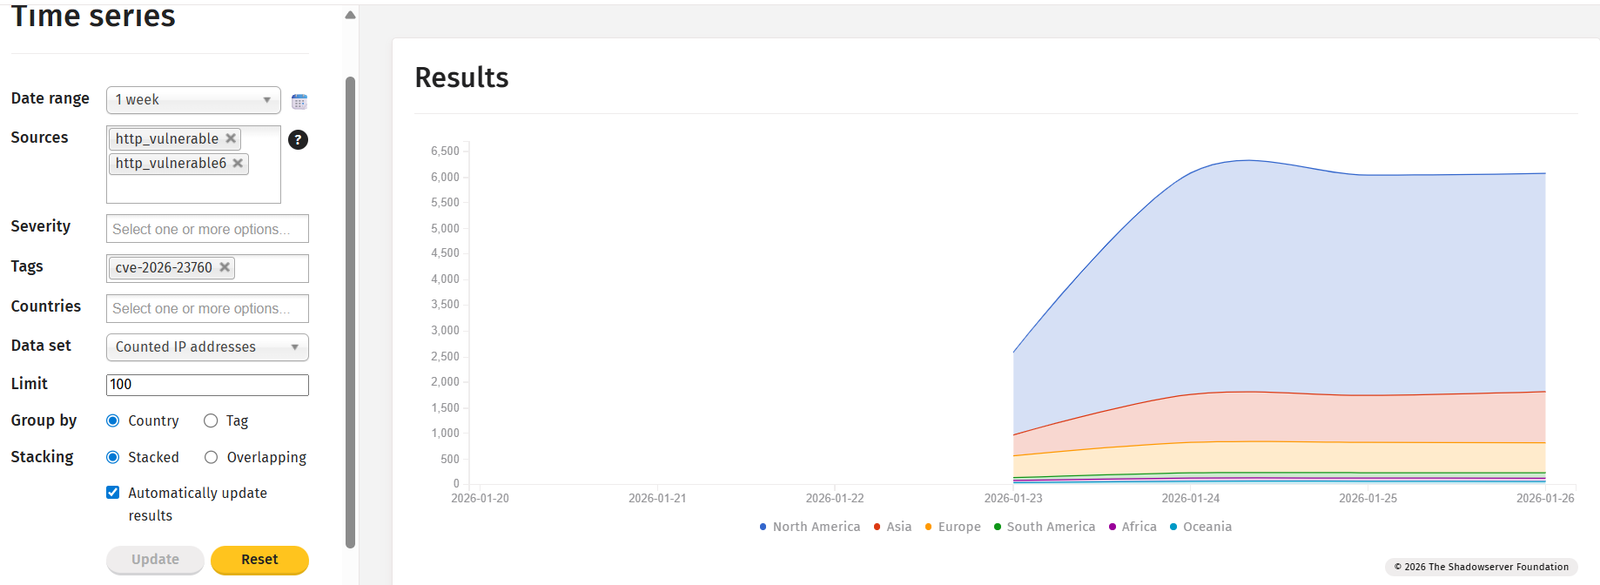
Shadowserver reported that over 6,000 SmarterMail servers are likely vulnerable, based on their version check. The researchers also observed exploitation attempts in attacks in the wild.
Most of the likely vulnerable servers are in the U.S. (4.1K), followed by Malaysia (449), India (188), Canada (166), and the U.K. (146).
Strategic Assessment: Russian Vostok Forces Hexacopter Operators Advance Along Eastern Front Operations
Tactical Overview: The Evolution of Heavy Hexacopter Operations Recent frontline reporting from…
Stacy Garrity Slams Shapiro Policies During High-Stakes Hatfield Datacenter Roundtable
As the 2026 Pennsylvania gubernatorial race heats up, the intersection of economic…
THE DEAD MMORPG SURVIVOR: How Dragon Nest Transformed Fast-Paced Action Combat—And Why Fans Refuse to Let It Die
LOS ANGELES, CA — Long before modern action RPGs dominated mainstream gaming…
Congressman Dan Meuser on Volpe
As lawmakers on Capitol Hill continue to navigate complex legislative battles over…
Massive Lane Closures on Route 38 in Cherry Hill Cause Major Delays
CHERRY HILL, N.J. — Commuters traveling through South Jersey this week are…

This week, CISA added CVE-2026-23760 to its KeV catalog, ordering FCEB agencies to address the identified vulnerability by February 16, 2026.