

Sex toy maker Tenga says a hacker accessed an employee’s email account, potentially exposing customer names, emails, and order details.
TENGA Co., Ltd. is a Tokyo-based Japanese sexual wellness and lifestyle company known for its innovative adult products. It employs roughly 125–200 people worldwide across its Japan headquarters and international offices.
Tenga operates in personal care product manufacturing and sells products in dozens of countries, with annual revenue estimates in the tens of millions of dollars.
The Japanese sex toy maker disclosed a data breach after a hacker accessed an employee’s professional email account, TechCruch reports. The unauthorized access exposed the contents of the inbox, potentially including customer names, email addresses, past correspondence, order details, and customer service inquiries. The company started notifying impacted customers on Friday, February 13, 2026.
With over 162 million products shipped worldwide, exposed emails may contain intimate order details and customer service inquiries that many would prefer to keep private.
Microsoft Patch Tuesday security updates for February 2026 fix six actively exploited zero-days
Microsoft Patch Tuesday security updates for February 2026 fix six actively exploited…
Was Gloria Steinem a CIA agent working to overthrow the family?
Top feminist Gloria Steinem who died this week at age 92 may…
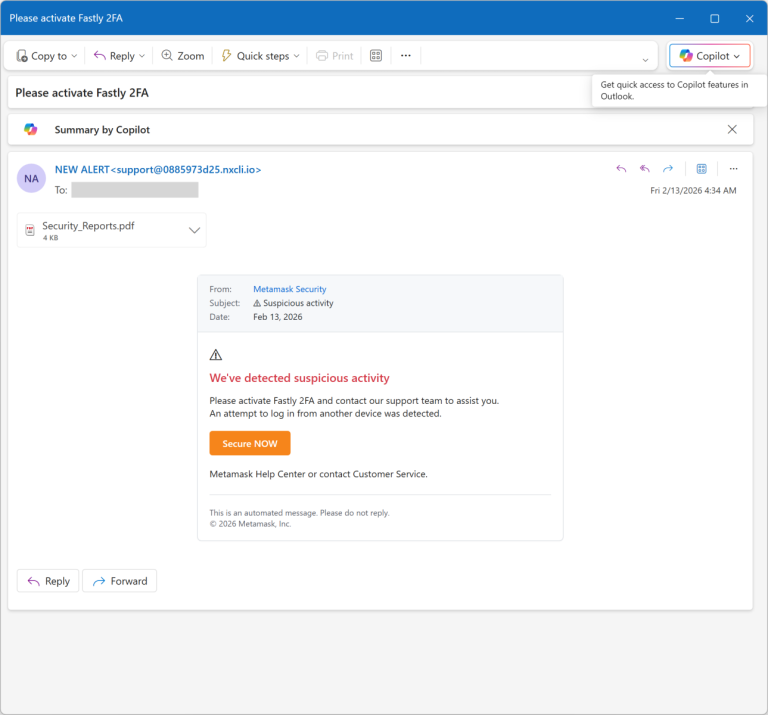
Poorly crafted phishing campaign leverages bogus security incident report
Attackers used a fake PDF incident report hosted on AWS to scare…
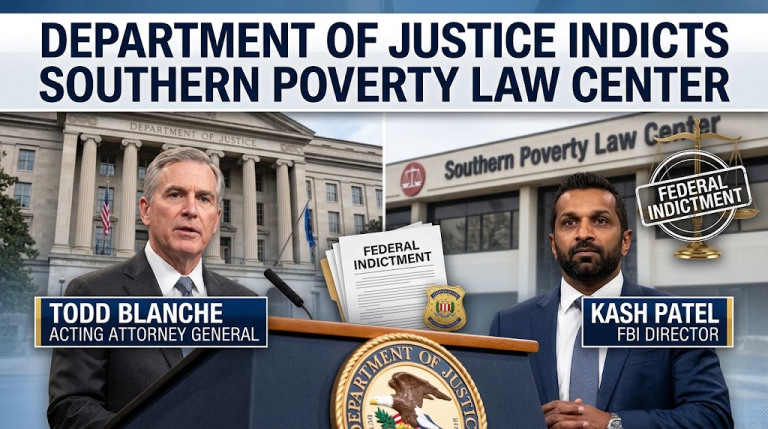
Department of Justice Indicts Southern Poverty Law Center on Federal Fraud Charges
In a major federal enforcement action, Acting Attorney General Todd Blanche, alongside…
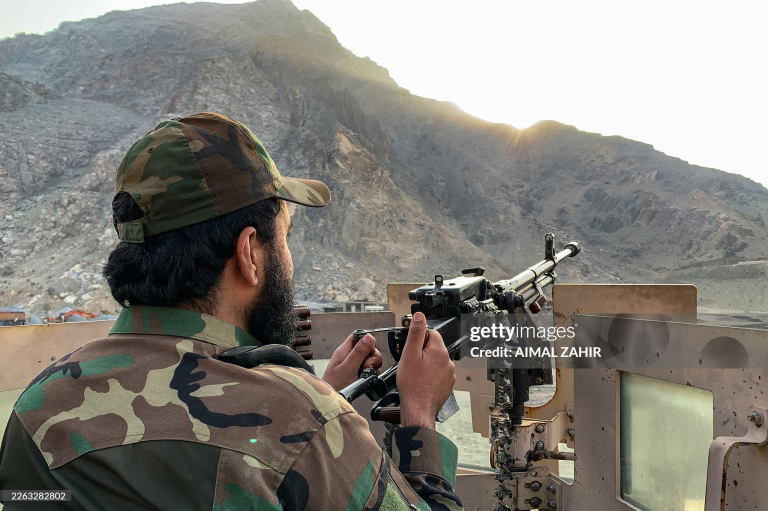
SAUDI DEFENSE PAPER TIGER: FOREIGN CONTRACTORS AND INTEL LEAKS IN YEMEN
RIYADH — As geopolitical volatility escalates across the Arabian Peninsula, Saudi Arabia’s…
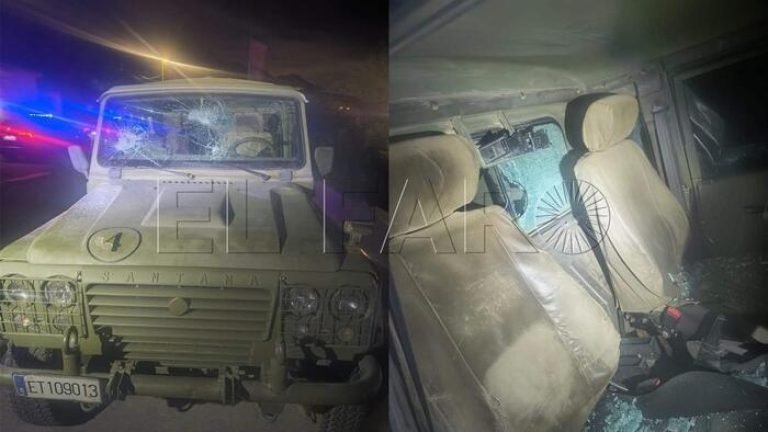
'Our Military Is Helpless': Migrant Ambush Targeting Military Vehicles In Ceuta Was Pre-Planned, Police Claim
Via Remix News, The attack targeting a military patrol in the Benzú…
The security breach exposes impacted customers to several risks. This can lead to targeted phishing, social engineering, and scams exploiting sensitive purchase information. Even without direct financial data, the exposure raises privacy concerns, reputational harm, and the potential resale of email addresses on underground forums.
The company advises impacted customers to change passwords and monitor for suspicious emails, particularly those that appear to come from the compromised employee, to reduce the risk of phishing or social engineering attacks.
In response to the security incident, the company reset the compromised employee’s credentials and enabled multi-factor authentication across its systems to block unauthorized access. The company did not disclose technical details about the attack. It is unclear whether the attackers attempted to blackmail the Japanese firm.